What Makes a File Share Secure? The Case for Files That Expire
Here's an exercise for anyone who uses Google Drive, Dropbox or OneDrive at work. Open the list of files you've shared by link and sort by date. Scroll to the bottom.
You'll probably find a contract from a deal that closed a long time ago, a spreadsheet you sent an accountant once, maybe a scan of someone's passport from an onboarding. Each link was created for one person, for one purpose that lasted a day or two. Each is still live.
That's not a failure of discipline. It's how cloud drives are designed. They're built to keep things, which is exactly what you want for a shared project folder and exactly what you don't want for a file that only needed to get from A to B.
The problem with "secure" file sharing today
When people say a file share is secure, they usually mean one of two things: it was sent over HTTPS, or the provider encrypts files on its disks. Both are good and both are standard. Neither addresses the main risk.
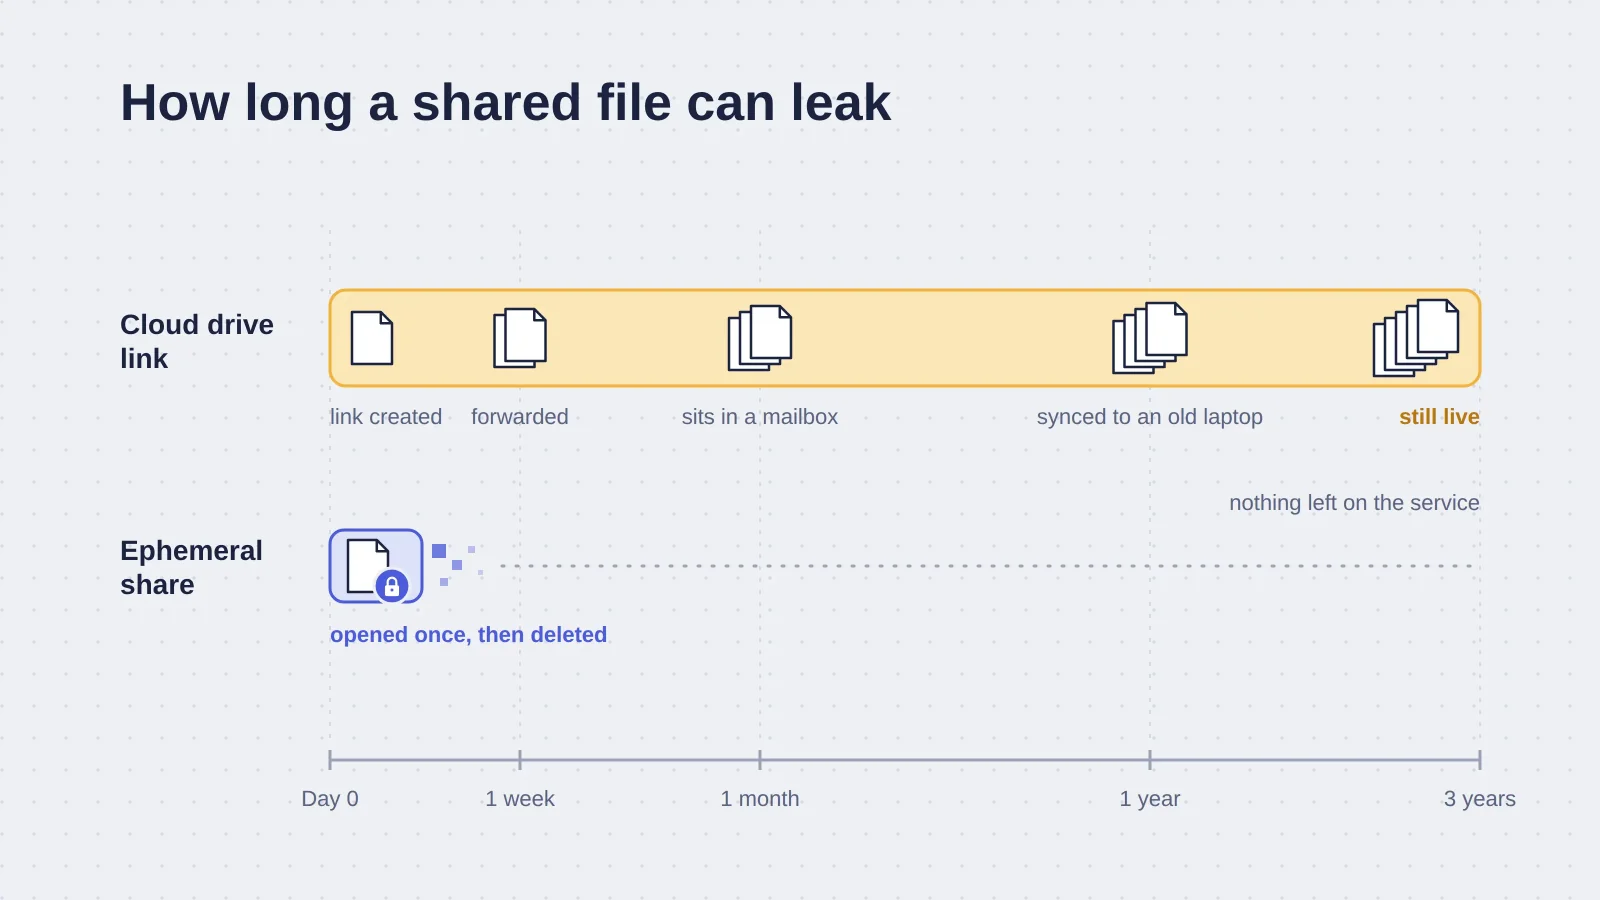
The main risk is time. A file that exists in five places for three years has many more chances to leak than a file that existed in one place for an hour. Every copy in a mailbox, every link that still works and every synced folder on an old laptop is something that can be breached, forwarded, or found by the wrong person later.
So a more useful definition of a secure file share has three parts:
- Only the recipient can read it, and ideally not even the service in between.
- It works once, so a forwarded or leaked link is useless after the intended person has opened it.
- It disappears, either after it's opened or after a deadline, whichever comes first.
The second and third parts are what people mean by ephemeral file sharing.
How ephemeral file sharing works
The mechanics are simple. Here's how it looks in Konfidant:
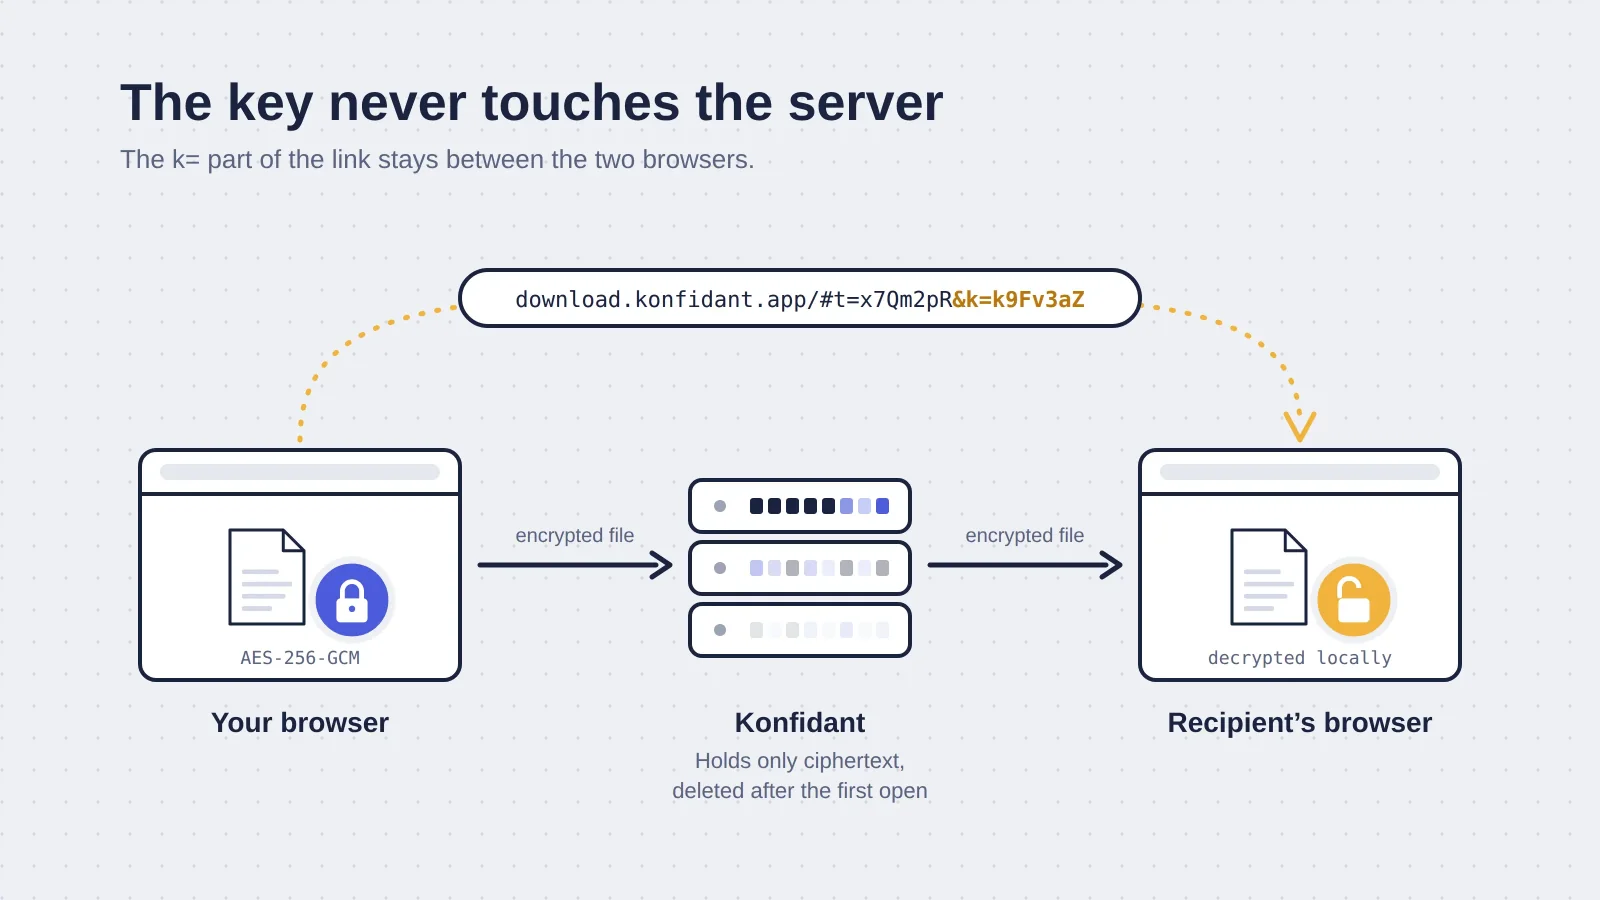
- You pick a file and an expiry time. Your browser encrypts the file (and its name) with a fresh AES-256-GCM key before uploading it.
- Konfidant stores the encrypted file and gives you a single-use link. The decryption key is in the part of the link after the
#, which browsers don't send to servers. Konfidant never has it. - You send the link to your recipient. They don't need an account.
- They click "Open & decrypt". Their browser downloads the encrypted file, decrypts it locally and saves it.
- The encrypted file is deleted from storage. The link now returns an error. If it's never opened, the same deletion happens at expiry.
From the recipient's side, it's a link and a download button. From the sender's side, it's one less file sitting in a drive for years.
Ephemeral sharing vs. a cloud drive link
| Cloud drive link | Ephemeral file share | |
|---|---|---|
| How long it lives | Until someone deletes it | Until it's opened or expires |
| Who can open the link | Anyone with it, as many times as they like (unless restricted) | The first person to open it, once |
| Can the provider read the file | Usually yes, they hold the keys | Not with client-side encryption |
| Good for | Ongoing collaboration, shared folders | One-off delivery of sensitive files |
| Copy left on the service afterwards | Yes | No |
To be fair to cloud drives: you can restrict links to specific accounts, set expiry dates on some plans and clean up shares regularly. If your team does all of that consistently, you're in good shape. Most teams don't, because every one of those steps is optional and manual.
When you need a file to expire
Ephemeral sharing earns its place whenever the file is sensitive and the job is delivery, not collaboration. Typical cases:
- Contracts and NDAs going to a client or counterparty for signature
- HR documents like offer letters, payslips and employment contracts
- Identity documents collected during onboarding or due diligence
- Financial records sent to an accountant, auditor or bank
- Credentials and config files handed to a developer or contractor
- Customer data exports sent to a vendor for a one-off job
The test I'd use: if the recipient is going to download this file and you'd prefer that no copy stays anywhere else, it's a candidate.
When it's the wrong tool
Ephemeral sharing is deliberately inflexible, and that cuts both ways.
- Collaboration. If several people need to edit a file, or come back to it next week, use a shared folder. A link that works once is a bad home for a living document.
- Large media. Konfidant handles files up to 5 MB on the free plan, 100 MB on Premium and 200 MB on Enterprise. If you're sending a 4 GB video, a dedicated large-file transfer service is a better fit.
- Records you must keep. Deleting the copy on the sharing service doesn't change your own retention duties. If you're legally required to keep a document, keep it in your own systems. Ephemeral sharing removes the extra copies, not the original.
- Public files. Brochures and price lists don't need any of this.
What to look for in a secure file share
If you're comparing tools, a few questions separate the serious ones:
- Is the file encrypted before it leaves my device? If not, the provider can read it.
- Can a link be opened more than once? For sensitive delivery, it shouldn't.
- What gets deleted, and when? The file itself, after delivery. Not just "access revoked".
- Do link previews or email scanners trigger the burn? They shouldn't. On Konfidant, the content is only released when the recipient clicks.
- Where is the data stored? Konfidant is hosted in Germany. Paid plans can store encrypted files in the EU or US; the free plan stores them in the US.
- Is there a data processing agreement? If you're sharing personal data in the EU, you need one. Konfidant's DPA is part of the Terms for every customer, so there's nothing extra to sign.
- Can the recipient use it without signing up? If they can't, people will go back to email attachments.
Getting a team to actually use it
The hardest part isn't the technology, it's the habit. People attach files to emails because it's one click. A few things help:
- Pick the three or four file types that matter most (contracts, payroll, IDs, credentials) and make a simple rule for those. You don't need to change how people share the lunch menu.
- Put the tool where people already are. A bookmark, a browser shortcut, a line in the onboarding doc.
- Use a custom domain if recipients are wary of unfamiliar links. On Konfidant's paid plans, links can come from something like
share.yourcompany.com. - Lead by example. When the person in charge of payroll sends payslips as one-time links, everyone else stops thinking of it as unusual.
Questions people ask
What is a secure file share?
A secure file share is a way to send a file so that only the intended recipient can read it, and so that no readable copy stays behind. In practice that means encryption before upload, a link that works once, and automatic deletion after the file is opened or the link expires.
Is an ephemeral file share the same as burn after reading?
Close. Burn after reading means the file is deleted after the first open. Ephemeral is the broader idea that the file has a limited life at all, which also covers expiry. Konfidant does both: whichever comes first. More on the mechanics in how self-destructing links work.
Can the recipient keep the file?
Yes. They download it, and it's theirs. What disappears is the copy on the service and the link that leads to it. No sharing tool can stop someone saving a file they've opened.
What if the recipient never opens it?
The link expires and the encrypted file is deleted. You'll need to send a new one.
Can I extend the expiry after sending?
No. Send a new link with a longer expiry. That's a deliberate trade-off: links that can be extended tend to get extended forever.
If you want to try sending a file that cleans up after itself, the free plan takes about a minute to set up. For concrete examples by team, see 10 situations where you need a secure file transfer.
This article provides general information, not legal advice. It describes Konfidant's features without guaranteeing them; what we provide is set out in our Terms of Service and Data Processing Agreement. Assess whether a tool meets your legal and regulatory requirements before sharing regulated data.
Enjoyed this article?
Get new articles on secrets management and secure sharing in your inbox. No spam, unsubscribe anytime.
We'll email you a link to confirm. Protected by Cloudflare Turnstile. See our Privacy Policy.
Ready to secure your team's secrets?
Stop leaving credentials in Slack. Start using burn-after-reading encryption.
Get started free