Burn After Reading: How Self-Destructing Links Actually Work
"This message will self-destruct in five seconds" is a great line for a spy film and a slightly misleading one for software. Nothing on your screen bursts into flames. What actually happens in a burn-after-reading system is quieter: a token gets marked as used, some bytes get deleted from a storage bucket, and a URL starts returning an error.
That quiet part is worth understanding, because it's where the difference between a real implementation and a cosmetic one lives. Some "self-destructing" tools hide the message in the interface and keep it on the server. Others delete the data but could have read it the whole time. This post walks through what a good one does, step by step, using Konfidant as the worked example, and is honest about what burn after reading can't do.
The short version
Burn after reading (also called burn-on-read, a one-time secret or a self-destructing link) means a shared message or file can be opened exactly once. After that first open, the link stops working and the content is deleted from the service.
Three properties make it useful:
- Single use. The first successful open consumes the link. A second attempt gets an error, not the content.
- Expiry. Links that are never opened still die after a set time, so a forgotten share doesn't sit around forever.
- Deletion. The stored content is actually removed, not just hidden.
A fourth property separates good implementations from the rest: the service can't read the content in the first place. If the provider holds the decryption key, "burn" only protects you from everyone except the provider and anyone who breaches them before the burn.
What happens, step by step
1. Encryption on the sender's device
When you paste a secret or drop a file into Konfidant, your browser generates a random 256-bit key just for that share. It encrypts the content with AES-256-GCM, including the file name and type, so those don't leak either. Large files are encrypted in authenticated chunks, which means the recipient's browser can detect any chunk that was modified, reordered or cut off.
The encrypted bytes are uploaded. The key is not.
If you use the API, the official SDKs (JavaScript, Go, Python, Ruby) do the same thing in your own code.
2. A single-use token from the server
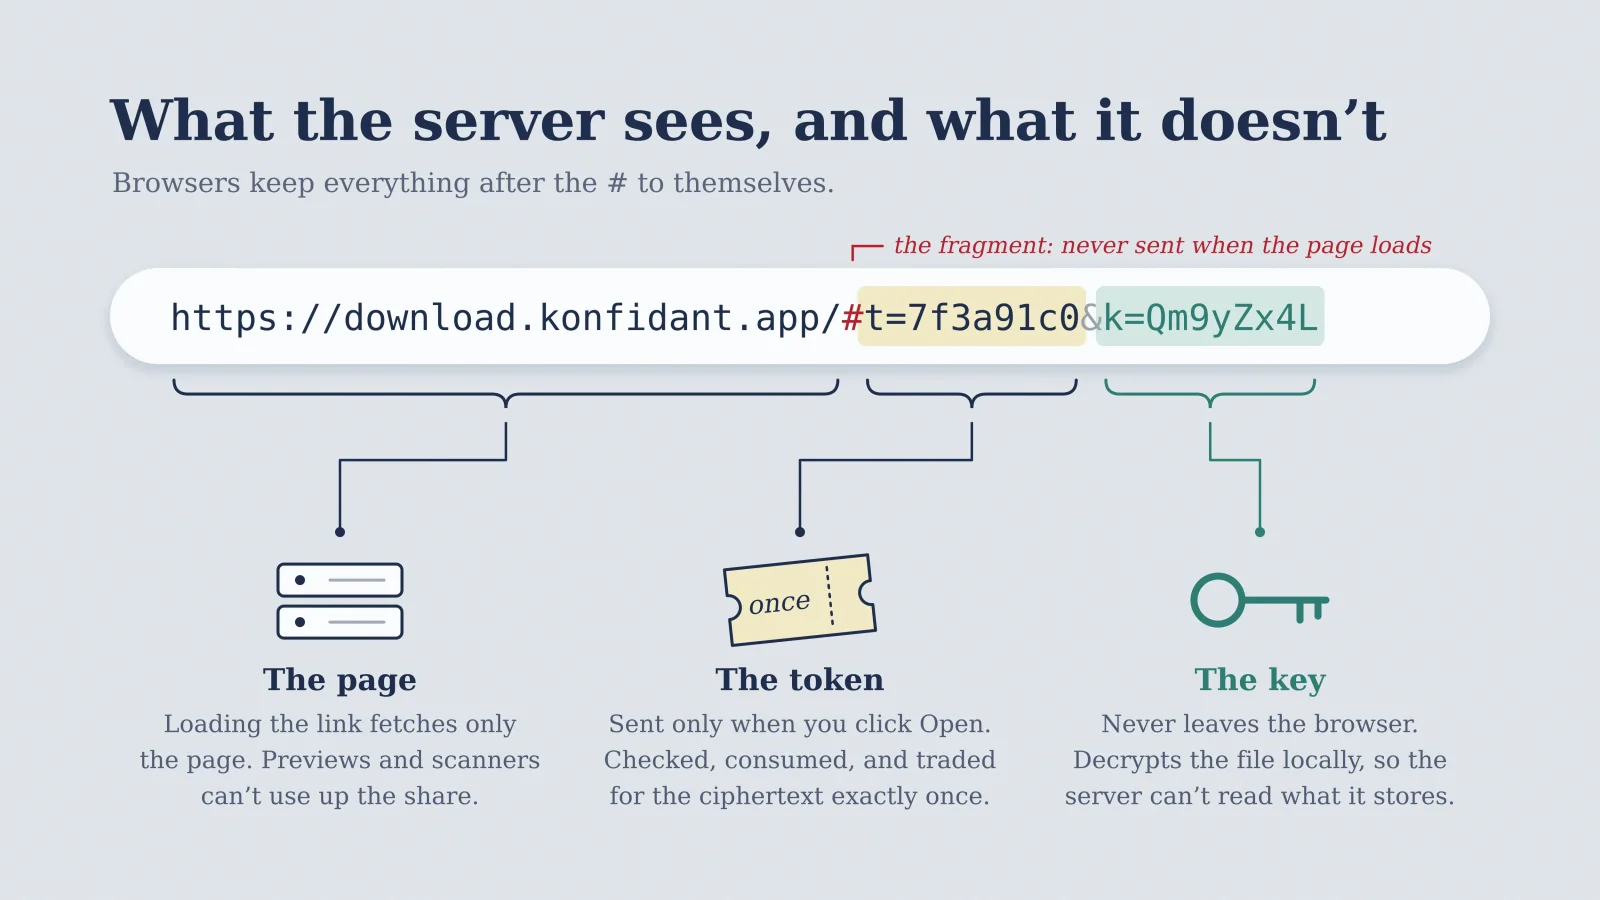
The server stores the ciphertext (files in object storage, short texts in a secrets vault) and issues a random, single-use token with an expiry time. The token is a ticket to download the ciphertext once. It doesn't contain the key and isn't enough to read anything on its own.
3. The link
Your browser combines the two into a link:
https://download.konfidant.app/#t=<token>&k=<key>
Everything after the # is the URL fragment. Browsers keep the fragment to themselves; it isn't sent to the server when the page loads. So the server only ever sees the token when the recipient uses it, and never sees k.
4. The open
The recipient opens the link and clicks "Open & decrypt". That click matters. Loading the page alone doesn't release anything, so a chat app's link preview or an email security scanner fetching the URL doesn't use up the share.
On click, the page sends the token to the server. The server checks it (valid, unused, unexpired) and consumes it in the same step, then returns the ciphertext. The browser decrypts it with the key from the fragment.
5. The burn
Right after delivery, the ciphertext is deleted from storage and the token is gone. Any later attempt with the same link returns 410 Gone. If the share is never opened, the same deletion happens at expiry.
That's it. No flames. But notice what the design buys you: at no point does the server hold anything it can decrypt, and after the open it doesn't even hold the ciphertext.
What burn after reading doesn't do
This is the section most product pages skip, and it's the one that keeps you out of trouble.
It doesn't stop the recipient from keeping a copy. Once someone has opened a secret, they can copy it, screenshot it or save the file. Burn after reading controls delivery, not what a person does afterwards. It isn't DRM, and anyone who tells you their link "can't be forwarded" means the link, not the content.
It doesn't protect a link before it's opened. Until that first click, the link is the secret. If you post it in a channel with 200 people, any of them can open it first. Send it to the person directly.
It doesn't make the content vanish from every system instantly. On Konfidant, file ciphertext is deleted on open. Text shares live in a secrets vault whose encrypted backups are kept for 7 days. Those backups are still ciphertext the server can't decrypt, but "nothing anywhere" would be an overstatement, and you should be suspicious of any service that claims it.
It doesn't hide that something was shared. The server knows a share of a certain size was created at a certain time and opened at a certain time. Like any website, it also has short-lived server and CDN logs with IP addresses (on Konfidant, deleted within 14 days and not linked to shares).
It can't fix a compromised device. If the sender's or recipient's machine has malware, encryption in the browser happens next to the malware. No sharing tool solves that.
Why it's still worth it
With those limits in mind, burn after reading still changes the risk in a meaningful way.
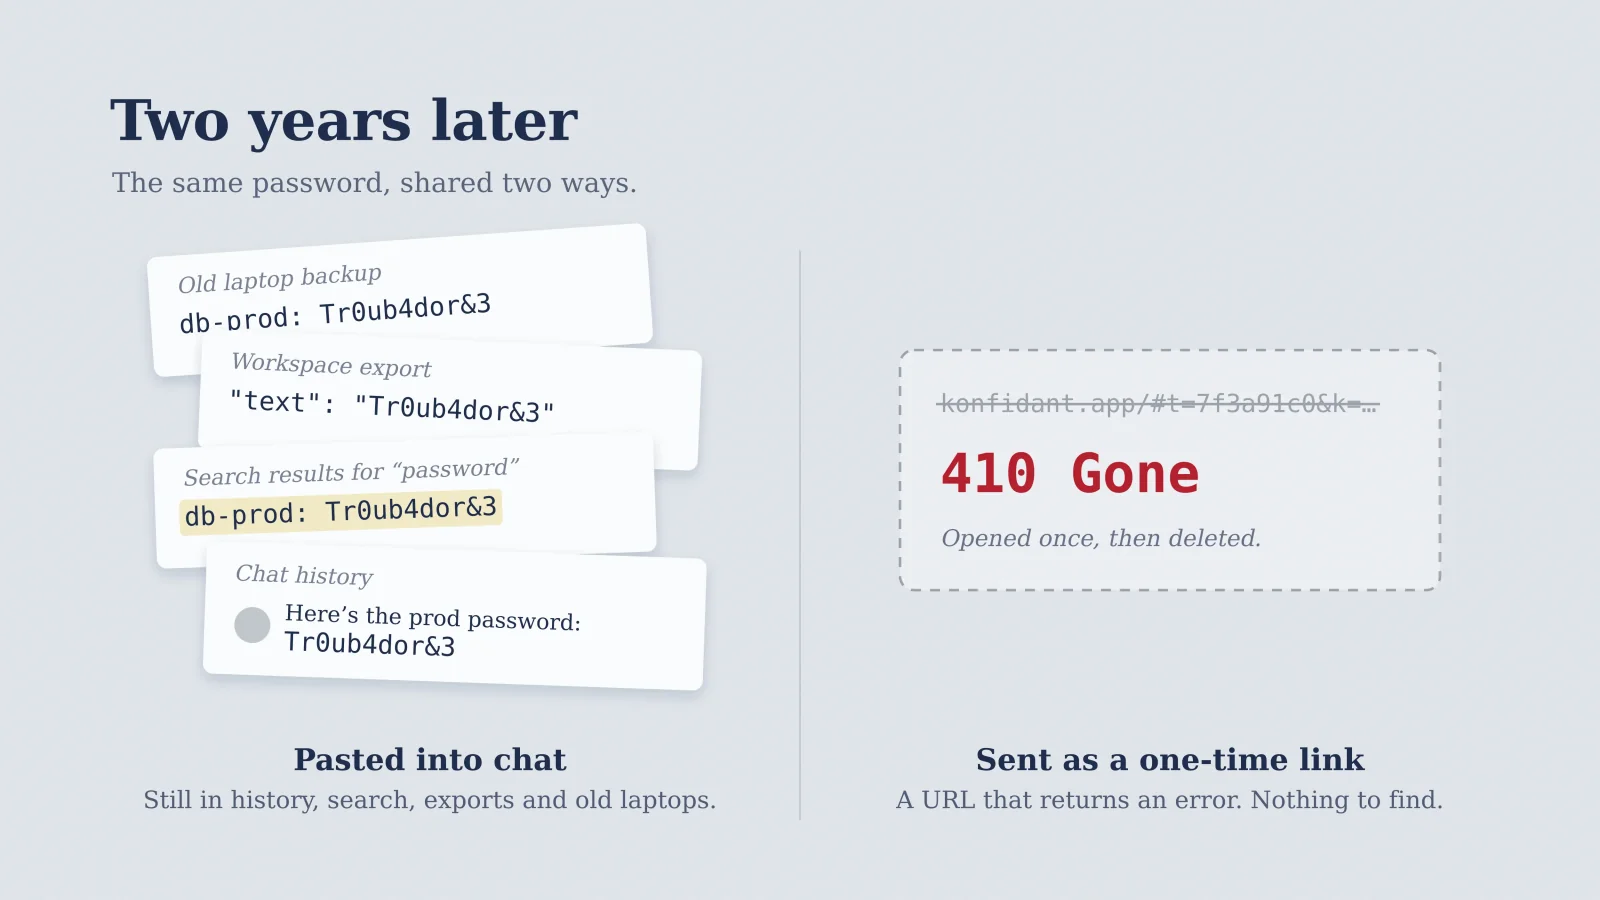
Think about where a password pasted into Slack is two years from now: in the workspace history, in search, in exports, on old laptops. Now think about a one-time link to the same password two years from now: a URL that returns an error. The secret existed in transit for minutes, not years.
That matters for three practical reasons:
- Breaches look backwards. An attacker who gets into a mailbox or a chat workspace searches the history. Burned links in that history are dead ends.
- Data minimization is a real obligation. GDPR expects you not to keep personal data longer than needed. A sharing step that deletes itself after delivery is an easy way to stop creating extra copies.
- You get a tamper signal. If your recipient opens the link and it's already been used, you know someone else got there. Plain-text sharing never tells you that.
How to tell a real implementation from a cosmetic one
If you're evaluating a burn-after-reading tool, these questions get to the truth quickly:
- Where is the content encrypted? "In your browser or SDK, before upload" is the answer you want. "At rest on our servers" means they hold the keys.
- Where does the key live? In the link fragment, or in your own code. Not in the provider's database.
- What does "burn" delete? The actual stored data, or just a flag that hides it in the UI?
- What happens to unopened shares? They should expire and be deleted, with a maximum lifetime you can control.
- Do link previews burn it? If posting the link in Slack or Outlook consumes it, you'll get a lot of confused "the link was already used" messages.
- Is the format documented? Konfidant's encryption format (KNF1) is documented with test vectors, so anyone can check that the SDKs do what we say.
Where it fits
Burn after reading is the right tool for things that need to arrive, not stay:
- passwords, API keys and other credentials handed to one person
- signed contracts and NDAs sent to a counterparty
- payroll documents, ID scans and other personal data
- bank details for a payment, sent once
- recovery codes and config files during an incident
It's the wrong tool for anything people need to come back to: shared project folders, documents you edit together, files that need version history. Use a normal drive for those.
Questions people ask
What happens if the recipient never opens the link?
It expires and the stored ciphertext is deleted. On Konfidant the maximum lifetime is 8 hours on the free plan, 7 days on Premium and 30 days on Enterprise.
Can I unsend a link?
There's no revoke button. If you sent the wrong thing, open the link yourself. That burns it, and your recipient will see a used link.
Can I find out when it was opened?
On the Enterprise plan, verified burn records the time each share was opened. It doesn't record who opened it or from where.
Can search engines index burn-after-reading links?
The tokens are random, so there's nothing to guess, and the content is only released on an explicit click. But never post one publicly: the first person to open it wins.
Is a one-time secret the same as an encrypted message?
Not necessarily. Encryption is about who can read it; one-time is about how many times it can be read. You want both. A good one-time secret tool encrypts on your device so the provider can't read it either.
If you'd like to see it in action, create a free account and send yourself a one-time secret. Then open the link twice. For the cryptography in more depth, see how end-to-end encrypted file transfer works.
This article provides general information, not legal advice. It describes Konfidant's features without guaranteeing them; what we provide is set out in our Terms of Service and Data Processing Agreement. Assess whether a tool meets your legal and regulatory requirements before sharing regulated data.
Enjoyed this article?
Get new articles on secrets management and secure sharing in your inbox. No spam, unsubscribe anytime.
We'll email you a link to confirm. Protected by Cloudflare Turnstile. See our Privacy Policy.
Ready to secure your team's secrets?
Stop leaving credentials in Slack. Start using burn-after-reading encryption.
Get started free