End-to-End Encrypted File Transfer, Explained Without the Marketing
Almost every file sharing service says your files are encrypted. It's on the pricing page, usually next to a padlock. And it's almost always true, in a way that tells you very little.
The question that actually matters is shorter: who holds the key? If the service holds the key, it can decrypt your files. So can anyone who breaches it, and anyone inside it with enough access. Encryption still helps (a stolen hard drive is useless, for example), but it's protecting the files from people who aren't the provider.
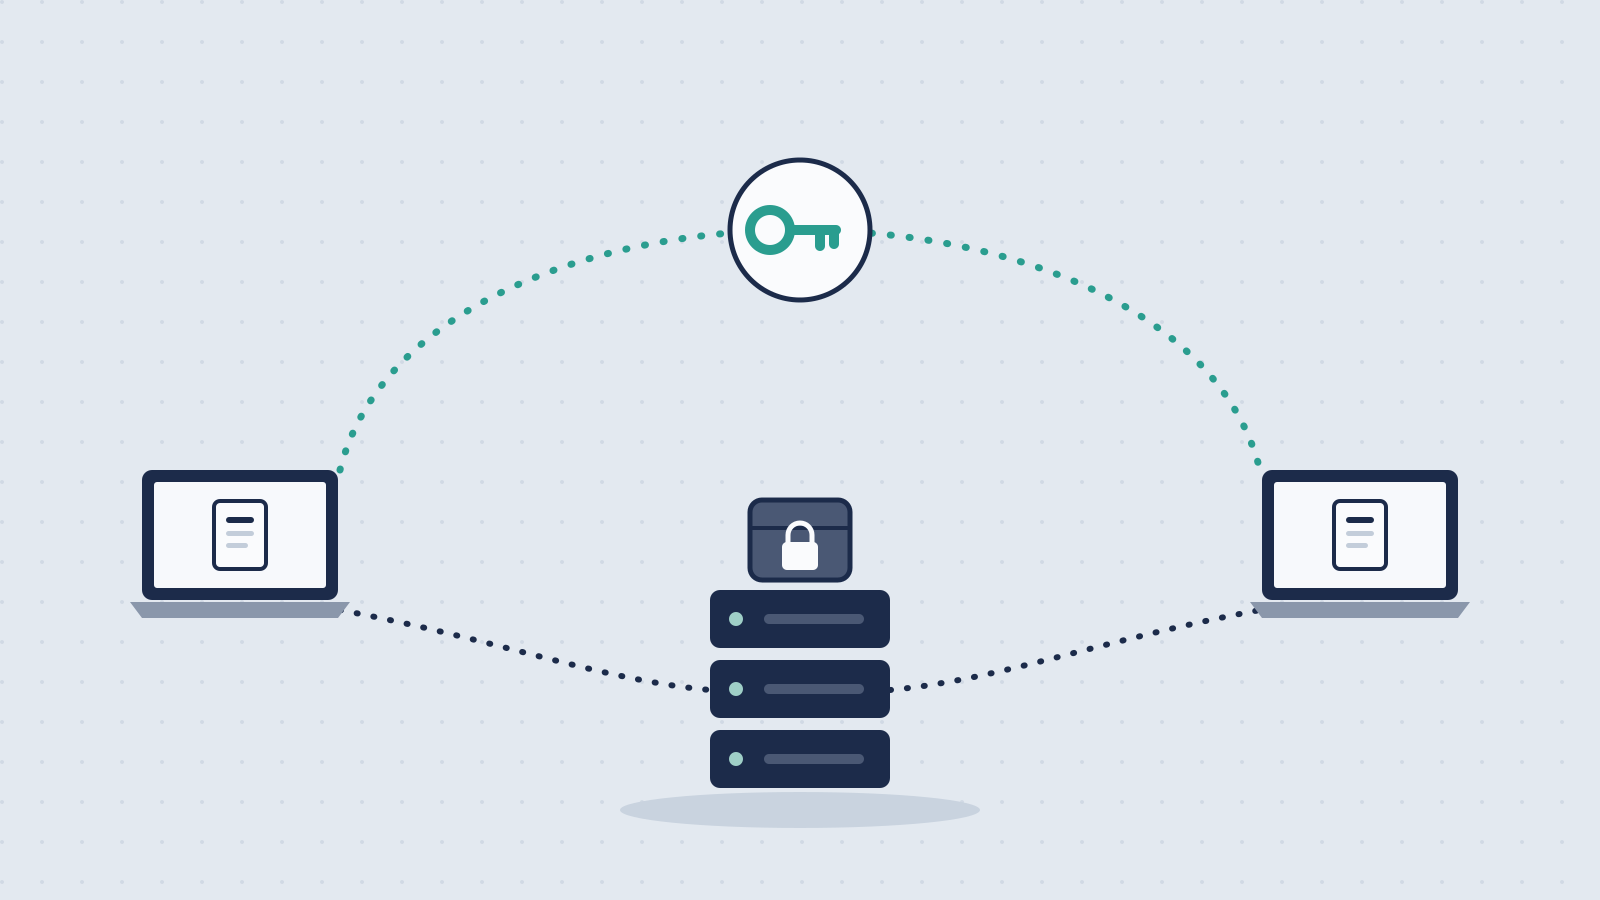
End-to-end encryption is the version where the provider doesn't hold the key. This post explains what that means for encrypted file transfer, how Konfidant does it, and what it doesn't protect you from. No marketing padlocks.
Three kinds of "encrypted"
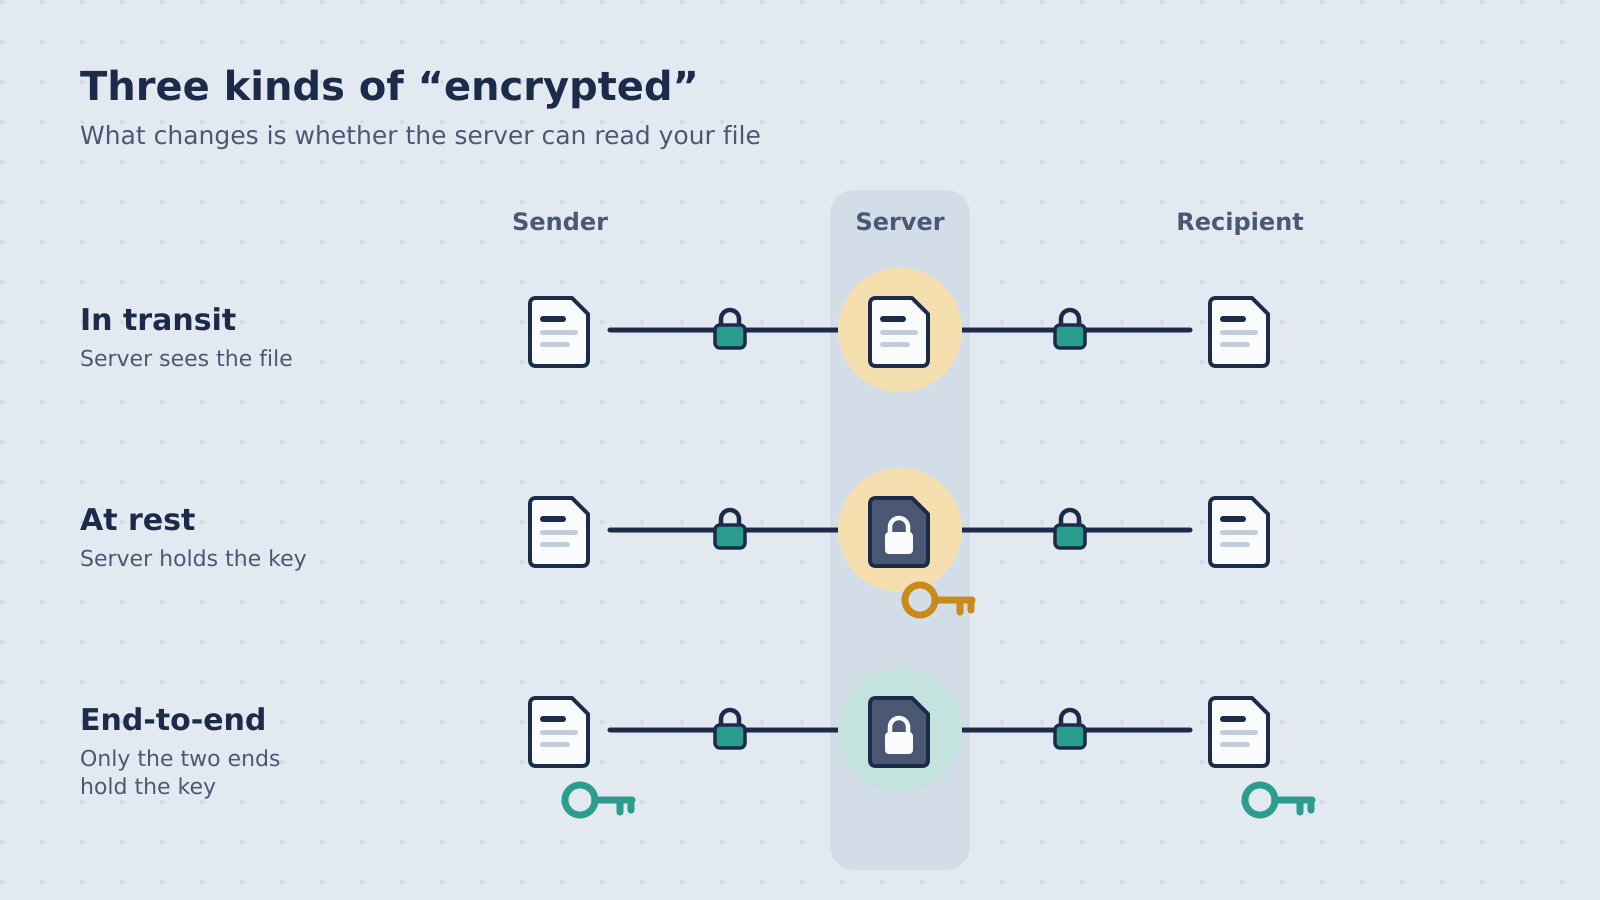
When a service says your files are encrypted, it usually means one or more of these:
Encryption in transit. Your file is protected by HTTPS (TLS) while it travels between your browser and the server. Every reputable service does this. It stops someone on the café Wi-Fi from reading your upload. Once the file arrives, it's decrypted and the server has the plaintext.
Encryption at rest. The server encrypts the file before writing it to disk, with a key the server manages. This protects against stolen disks and some kinds of storage leaks. But the server can decrypt whenever it needs to, because it has the key. Most cloud drives work like this.
End-to-end encryption. The file is encrypted on the sender's device, before upload, and only decrypted on the recipient's device. The key travels from sender to recipient without the server ever seeing it. The server stores and delivers bytes it can't read.
The first two are standard hygiene. The third is what changes who you have to trust.
How end-to-end encrypted file transfer works in Konfidant
Here is the whole flow, from the moment you pick a file to the moment it's gone.
On the sender's device
Your browser (or one of the official SDKs if you use the Konfidant API) generates a random 256-bit key. It's used for this one share and never again.
The file is encrypted with AES-256-GCM, a widely used authenticated cipher. "Authenticated" means that if anyone changes even one bit of the encrypted data, decryption fails loudly instead of producing corrupted output. The file name and type are encrypted along with the contents, so the server doesn't learn those either.
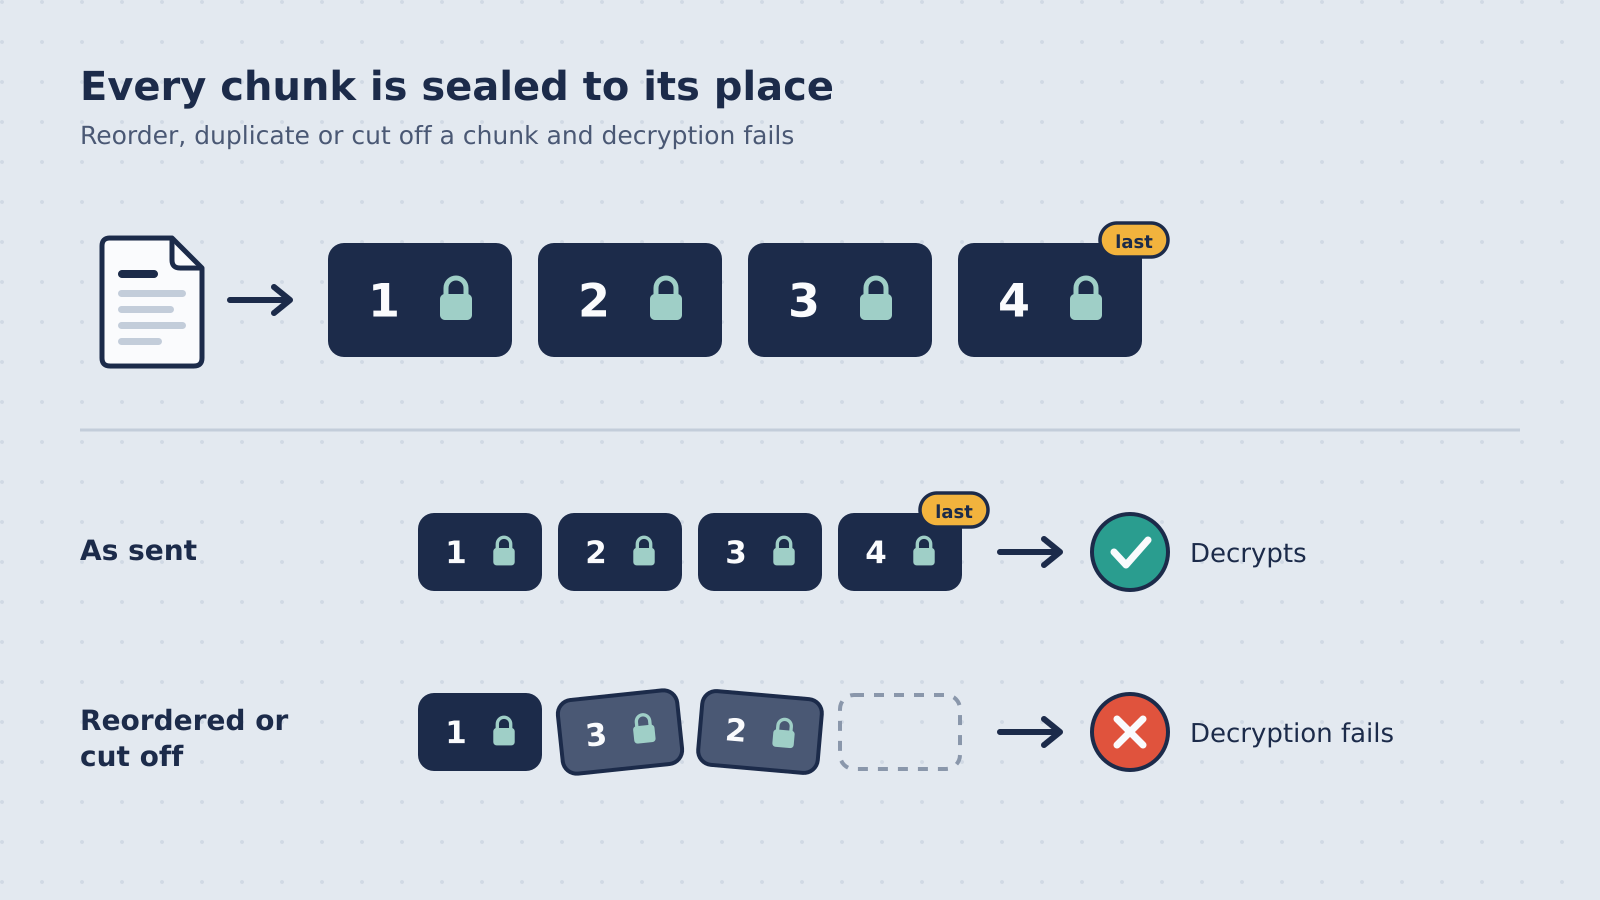
Larger files are encrypted in chunks, and each chunk is tied to its position and to whether it's the last one. That stops anyone from reordering, duplicating or cutting off chunks without the recipient noticing. The format is called KNF1, and it's documented with test vectors so the SDKs and the browser produce byte-for-byte identical results.
Only the encrypted bytes are uploaded.
In the link
Konfidant gives back a single-use token. Your browser combines it with the key into a link:
https://download.konfidant.app/#t=<token>&k=<key>
Everything after the # is the URL fragment. This is the clever-but-boring bit that makes the whole thing work: browsers don't send the fragment to the server when they load a page. It stays in the browser. So the key travels inside the link, from you to your recipient, and never touches Konfidant's servers or logs.
On the recipient's device
The recipient opens the link. The page reads the fragment locally, and when they click "Open & decrypt", it sends only the token to the server. The server checks the token, consumes it, and sends back the encrypted file. The recipient's browser decrypts it with the key and saves the result.
Right after that, the encrypted file is deleted from storage, and the link is dead.
What the server sees
Put together, Konfidant's servers know:
- that a share of a certain size was created at a certain time
- when it was opened
- the account that created it
They don't know the contents, the file name, the file type or the key. Like any website, the servers and CDN keep short-lived access logs with IP addresses; Konfidant deletes them within 14 days and doesn't link them to shares.
Why this matters in practice
It's tempting to treat end-to-end encryption as a box to tick. It's more useful to think about specific bad days.
A breach. If someone got full access to Konfidant's database and storage, they'd find ciphertext and tokens. Without the keys, which were never there, it's noise.
An insider. No one operating the service can read your files, because there's nothing on the server to read them with. You don't have to trust anyone's good intentions.
A misconfiguration. Storage buckets get exposed by accident across the industry every year. An exposed bucket of client-side encrypted files is an embarrassment, not a data breach.
This is also why burn-on-read deletion and encryption work well together. Deletion shrinks the time the ciphertext exists. Encryption makes the ciphertext useless while it does. More on the deletion side in how burn-after-reading links work.
The limits, honestly
End-to-end encryption is strong, but it's not magic. Here's what it doesn't cover.
You trust the code that does the encrypting. In a web app, that code is JavaScript the service sends to your browser. A malicious or compromised service could, in principle, send code that leaks the key. Konfidant reduces that risk: download pages load no third-party scripts at all (no analytics, no chat widgets) and run under a strict, nonce-based Content Security Policy. If you want to remove the trust assumption entirely, use the SDKs. They're open on GitHub, they encrypt in your own process, and Konfidant never sees the plaintext or the key.
Endpoints still matter. If the sender's or recipient's computer has malware, it can read the file before encryption or after decryption. No transfer tool fixes that.
The link is the key. Anyone who gets the full link before your recipient opens it can open it themselves. Send it directly to the person, not to a group chat or a shared mailbox.
The recipient can keep the file. Encryption controls who can read it in transit. It doesn't control what someone does after they've legitimately opened it.
Metadata exists. The server knows the size and timing of shares. For most business use that's harmless, but it's not zero.
How to check a provider's encryption claims
If you're evaluating any service that promises encrypted file transfer, four questions cut through the marketing:
- Where does encryption happen? In your browser or app before upload, or on their server after?
- Where is the key? If they can reset your access and still show you your files, they have it.
- Can their support staff see my files? If the honest answer is "only with permission", they can.
- Is the format documented? Standard algorithms, a published format, and ideally clients you can read. Proprietary crypto is a red flag.
Questions people ask
Is HTTPS the same as end-to-end encryption?
No. HTTPS protects the connection between you and the server. The server still receives your file in readable form. End-to-end encryption means the server only ever receives the encrypted version.
Is AES-256 actually secure?
Yes. AES is a public standard, it's been studied for over two decades, and there's no known practical attack on AES-256 when it's used correctly. The weak points in real systems are almost always key handling and implementation, which is why where the key lives matters more than which cipher is used.
What about quantum computers?
The known quantum attack on symmetric ciphers (Grover's algorithm) roughly halves the effective key strength, which still leaves AES-256 with a very large safety margin. The bigger open question is public-key cryptography, such as the TLS connections that carry data across the internet. Browsers and major providers are already rolling out post-quantum key exchange for TLS, so that part is being addressed at the internet level.
What if I lose the link?
Then the file can't be recovered by anyone, including Konfidant. That's the trade-off of the provider not holding the key. Send a new link.
Can I send encrypted files without the recipient installing anything?
Yes. Recipients just need a modern browser. Decryption uses the browser's built-in Web Crypto API.
If you'd like to send encrypted files your provider can't read, Konfidant's free plan works in any browser. Developers can find the SDKs and API reference in the docs.
This article provides general information, not legal advice. It describes Konfidant's features without guaranteeing them; what we provide is set out in our Terms of Service and Data Processing Agreement. Assess whether a tool meets your legal and regulatory requirements before sharing regulated data.
Enjoyed this article?
Get new articles on secrets management and secure sharing in your inbox. No spam, unsubscribe anytime.
We'll email you a link to confirm. Protected by Cloudflare Turnstile. See our Privacy Policy.
Ready to secure your team's secrets?
Stop leaving credentials in Slack. Start using burn-after-reading encryption.
Get started free