Security for Remote Teams: A Practical Playbook for Sharing Files and Access
In an office, a lot of sensitive information never gets written down. Someone walks over to your desk and reads out the Wi-Fi password. The contract gets printed and signed in the meeting room. The new hire gets their laptop from IT, in person, with the logins on a sticky note that ends up in the bin.
Remote teams don't have any of that. Everything that used to be said out loud now goes through Slack, email or a shared drive, which means it's written down, stored and searchable. That's mostly a good thing for collaboration. It's also why remote teams tend to accumulate sensitive data in places nobody's watching.
This playbook is for small and mid-sized teams without a dedicated security department. It's ordered by what gives you the most protection for the least effort.
Start with accounts: MFA and a password manager
Before anything else, two basics. They're boring, and they prevent a large share of real-world incidents.
Turn on multi-factor authentication everywhere that matters: email, chat, your identity provider, cloud consoles, code hosting, finance tools. Prefer authenticator apps or security keys over SMS codes. If your company uses Google Workspace or Microsoft 365, you can enforce this for everyone from the admin console.
Give everyone a password manager, and pay for the business version so you can share vaults and remove access when people leave. This single change removes most of the reasons people paste passwords into chat.
If you only do these two things this quarter, you've done more than most.
Decide how sensitive documents travel
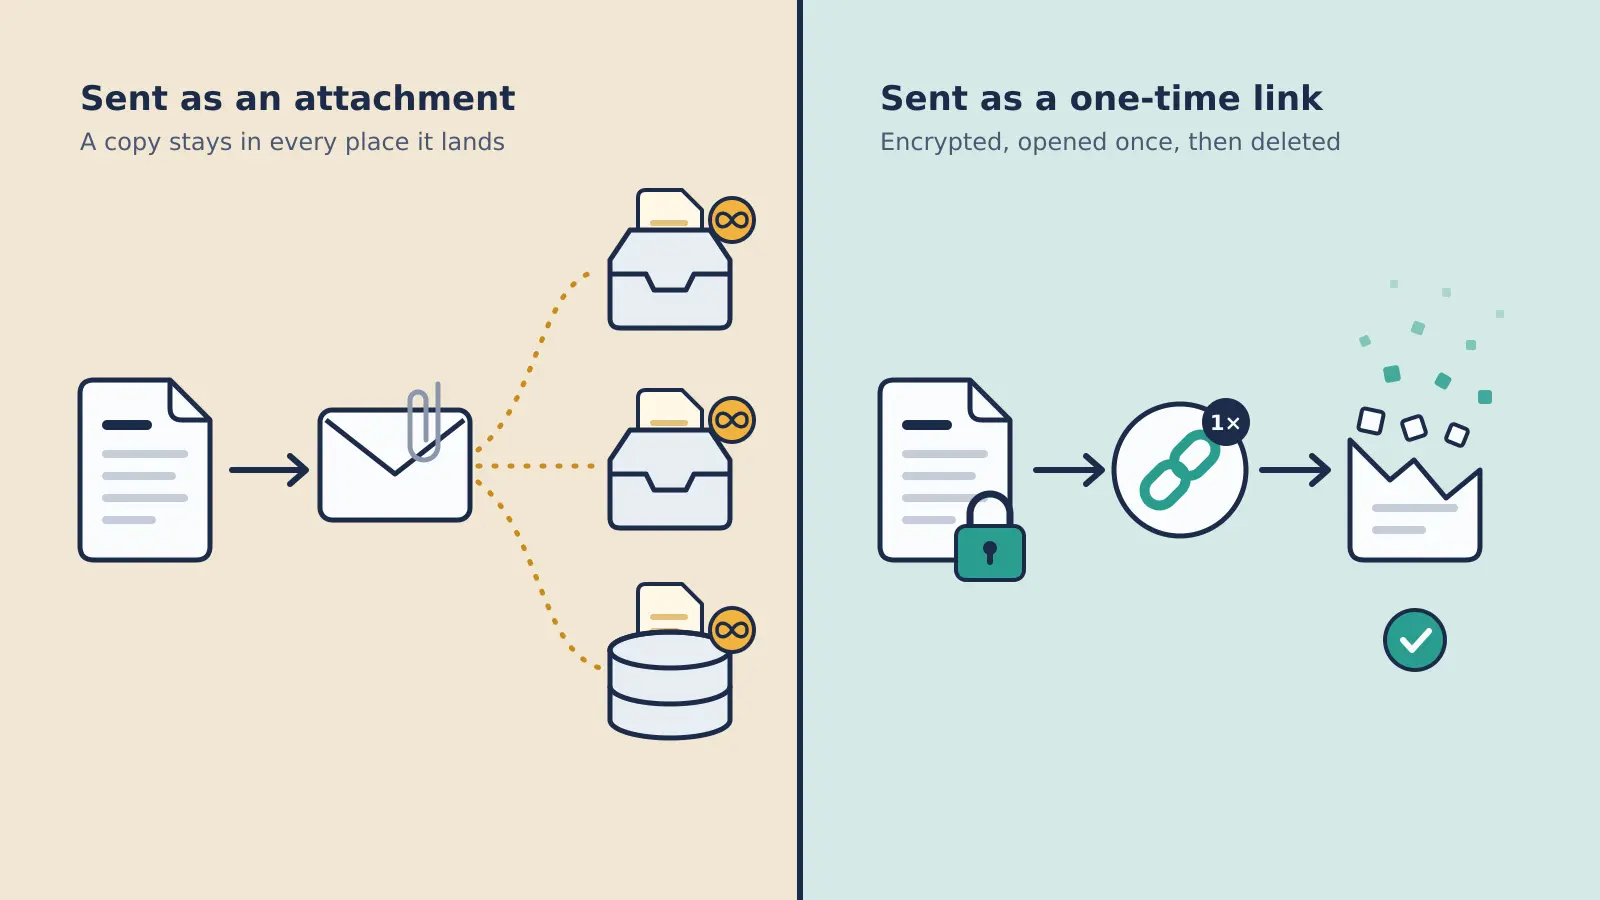
The second big source of risk on remote teams is how documents move around. Without a shared office, every contract, payslip, ID scan and customer export travels as an email attachment or a cloud link, and stays wherever it lands.
You don't need a policy for every file. You need one for the handful of document types that would hurt if they leaked. A good starting list:
- contracts, NDAs and anything under legal privilege
- offer letters, payslips and other HR documents
- passport and ID scans
- financial statements and bank details
- credentials, keys and config files
- customer data exports
For each, the question is whether the document is being collaborated on or delivered.
Collaboration belongs in your shared drive or document system, with access restricted to named people and reviewed now and then.
Delivery (sending a file to someone so they have it) is where most leaks come from, because the default tools keep a copy forever. Email stores it in every mailbox and backup. Drive links work until someone remembers to turn them off. For these, use a secure document sharing platform that encrypts the file before upload, gives you a link that works once, and deletes the file after it's opened. That's what Konfidant is built for.
The rule your team needs fits in a sentence: if it's on the list and you're sending it to someone, send a one-time link, not an attachment.
Share credentials without leaving them in chat
Remote teams share credentials all the time: the staging database for a new developer, the shared social media login, the vendor portal nobody wanted to pay extra seats for. In an office, some of that would have been said out loud. Remotely, it's typed into a DM, where it stays.
Three tools cover almost every case:
- Individual accounts and SSO, wherever the tool supports it. These are the only clean way to remove someone later.
- A password manager for credentials several people use regularly.
- One-time secret links for credentials someone needs once, especially people outside your password manager like contractors and vendors.
If you want the details, there are separate guides on sharing passwords and sharing API keys.
One remote-specific tip: incidents and on-call. When something breaks at 2 am, credentials get pasted into whatever channel is open. Add "rotate any credentials shared during the incident" to your incident checklist, so cleanup happens even when the sharing wasn't ideal.
Look after the devices
Remote work means company data lives on laptops in homes, cafés and trains. You can't control the network, so focus on the device:
- Full-disk encryption on. FileVault on macOS and BitLocker on Windows are built in. A stolen laptop with disk encryption is a hardware loss, not a data breach.
- Automatic updates on, for the operating system and the browser at minimum.
- Screen lock after a few minutes, with a password or biometrics.
- A way to see and wipe company devices, if you're large enough to justify a device management tool. Even a simple inventory of who has which laptop helps.
Personal devices are harder. If people check work email on their own phones, require a passcode and use the managed-app features your email provider offers. Avoid company data sitting in personal cloud accounts.
Rethink the network, briefly
The old model was a trusted office network behind a firewall. Remote teams don't have one, and recreating it with a VPN for everything is often more trouble than it's worth.
Most modern advice (usually called zero trust) comes down to this: don't trust a request because of where it comes from, trust it because of who's making it and from what device. In practice, for a small team, that mostly means SSO with MFA in front of your important tools, and making sure those tools are configured to require it. A VPN is still useful for reaching internal systems that aren't on the internet; it isn't a substitute for strong authentication.
Make offboarding a checklist, not a memory exercise
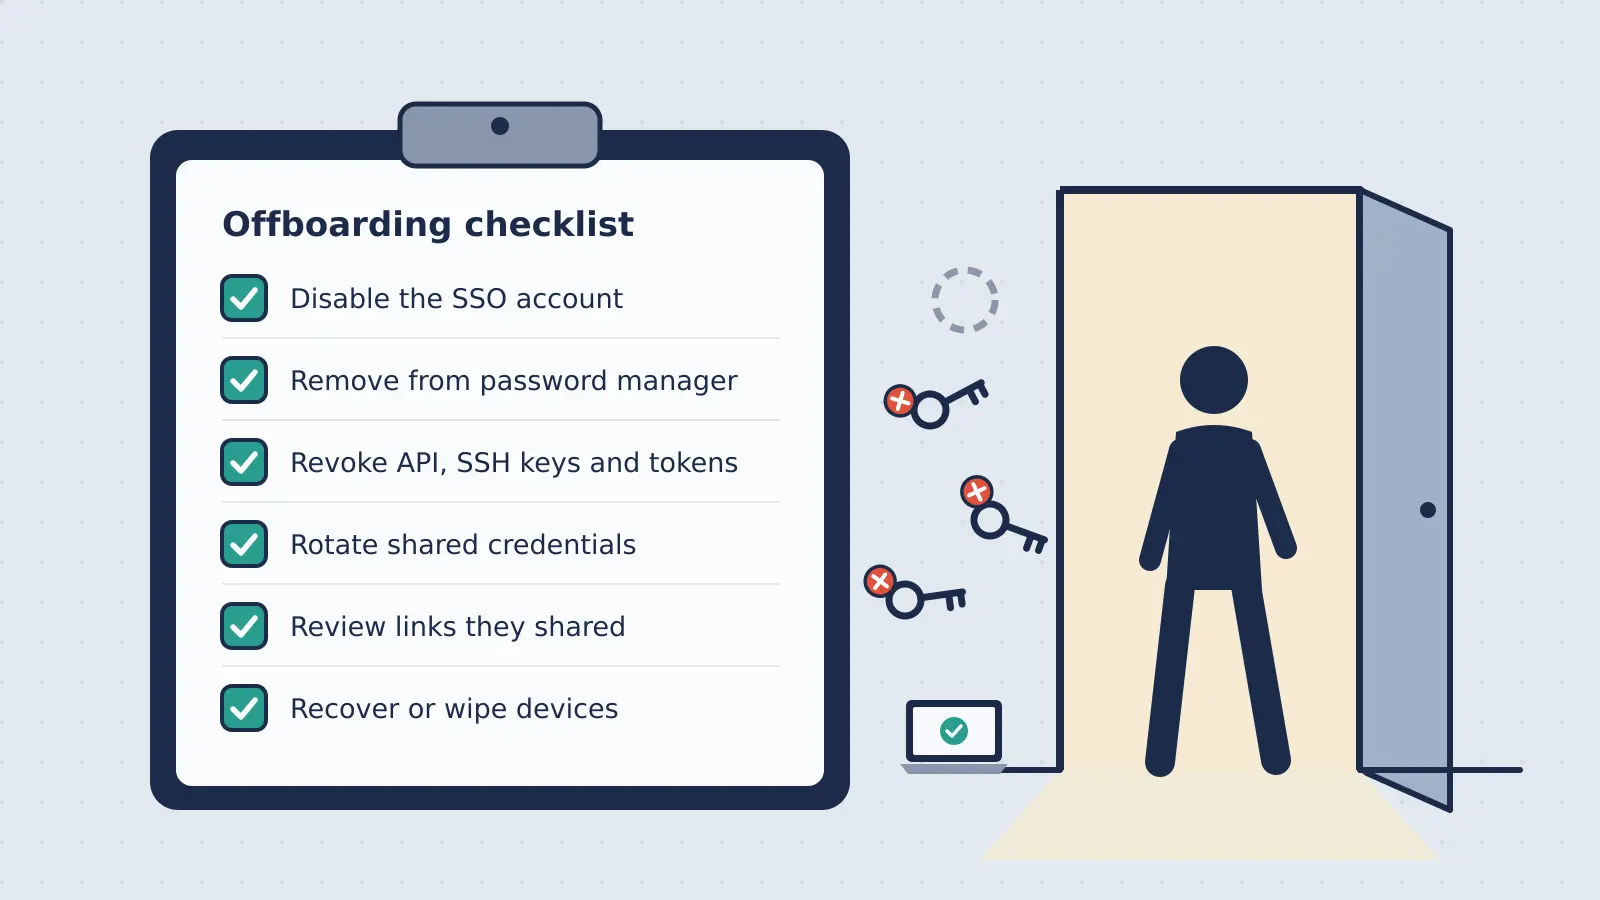
Offboarding is where remote teams leak the most access, quietly. The person leaves, their laptop gets posted back eventually, and their access to a dozen tools is removed over several weeks, or never.
A short checklist fixes most of it:
- Disable the identity provider account first; SSO-connected tools follow.
- Remove them from the password manager and any shared vaults.
- Revoke personal API keys, tokens and SSH keys.
- Rotate shared credentials they knew, starting with the most sensitive.
- Review shared drive folders and links they owned.
- Recover or wipe company devices.
The last two get forgotten most. Files a former employee shared by link stay accessible after they've gone, unless someone turns those links off. This is one more reason to use one-time links for delivery: they don't outlive the person who sent them.
What to look for in a secure document sharing platform
If you're choosing a tool for sending sensitive documents, here's what makes a difference for distributed teams:
- Encryption before upload, so the provider can't read your files.
- Single-use links with expiry, so a forwarded or old link is useless.
- No account needed for recipients, so clients and candidates don't fall back to email.
- Team management and audit logs, so you know who on your team shared what, and can remove people cleanly.
- A custom domain, so recipients see
share.yourcompany.comand don't think it's phishing. - An API, if you want to send documents from your own systems. This is where secure sharing starts to overlap with enterprise file transfer.
- A data processing agreement and a clear storage location, especially if you handle personal data of people in the EU.
Konfidant covers these on its paid plans: Premium adds team management, audit logs, custom domains, the API and EU or US storage; Enterprise adds your own branding on download pages, verified burn (a record of when each share was opened) and longer link lifetimes. For bulk, scheduled transfers between systems, a managed file transfer product is the better fit.
Train people with examples, not slide decks
The best security training for a remote team is short and specific. Twenty minutes, once a quarter, with real examples from your own tools:
- what a phishing email aimed at your company looks like
- how to tell a real document-sharing link from a fake one
- what to do (and who to message) if you think you clicked something bad
- the one-sentence rules for documents and credentials
Make it safe to report mistakes. A teammate who says "I think I pasted the production key in the wrong channel" within five minutes is far more valuable than one who stays quiet out of embarrassment.
Questions people ask
What should a small remote team fix first?
MFA on email and chat, a business password manager, and a rule for sending sensitive documents. Those three cover a lot of ground for very little money.
Do we need a VPN?
Only if you have internal systems that aren't reachable otherwise. For SaaS tools, SSO with MFA does more than a VPN would.
How do we handle contractors?
Give them their own accounts with an end date, share only what they need, and use one-time links for any files or credentials you send them. Add them to your offboarding checklist like anyone else.
Is a cloud drive enough for secure file sharing?
For collaboration, usually yes, if access is restricted to named people. For delivering sensitive documents to someone, it's the wrong default, because links stay live until someone turns them off.
If you'd like your team to stop sending sensitive documents as attachments, start with Konfidant's free plan and upgrade when you're ready to add your team. For more on the reasoning, see 5 everyday sharing habits that leak sensitive data.
This article provides general information, not legal advice. It describes Konfidant's features without guaranteeing them; what we provide is set out in our Terms of Service and Data Processing Agreement. Assess whether a tool meets your legal and regulatory requirements before sharing regulated data.
Enjoyed this article?
Get new articles on secrets management and secure sharing in your inbox. No spam, unsubscribe anytime.
We'll email you a link to confirm. Protected by Cloudflare Turnstile. See our Privacy Policy.
Ready to secure your team's secrets?
Stop leaving credentials in Slack. Start using burn-after-reading encryption.
Get started free