Why Email Is the Wrong Place for Confidential Documents
Email has one superpower: it doesn't lose things. A message you sent in 2014 is probably still sitting in your sent folder, the recipient's inbox, two backup systems and a compliance archive. For a lunch invitation, that's harmless. For a signed contract, a payslip or a database password, it's a long-term liability that nobody signed up for.
This isn't a complaint about any particular provider. Gmail, Outlook and the rest are well run and well secured. The issue is what email is for. It was designed in the 1970s and 80s to deliver messages reliably between trusted academic computers, and every security feature since has been added on top of that design rather than built into it.
So if you're looking for secure document sharing, it helps to understand exactly where email falls short, and where it's perfectly fine.
Problem one: every email is a permanent copy, many times over
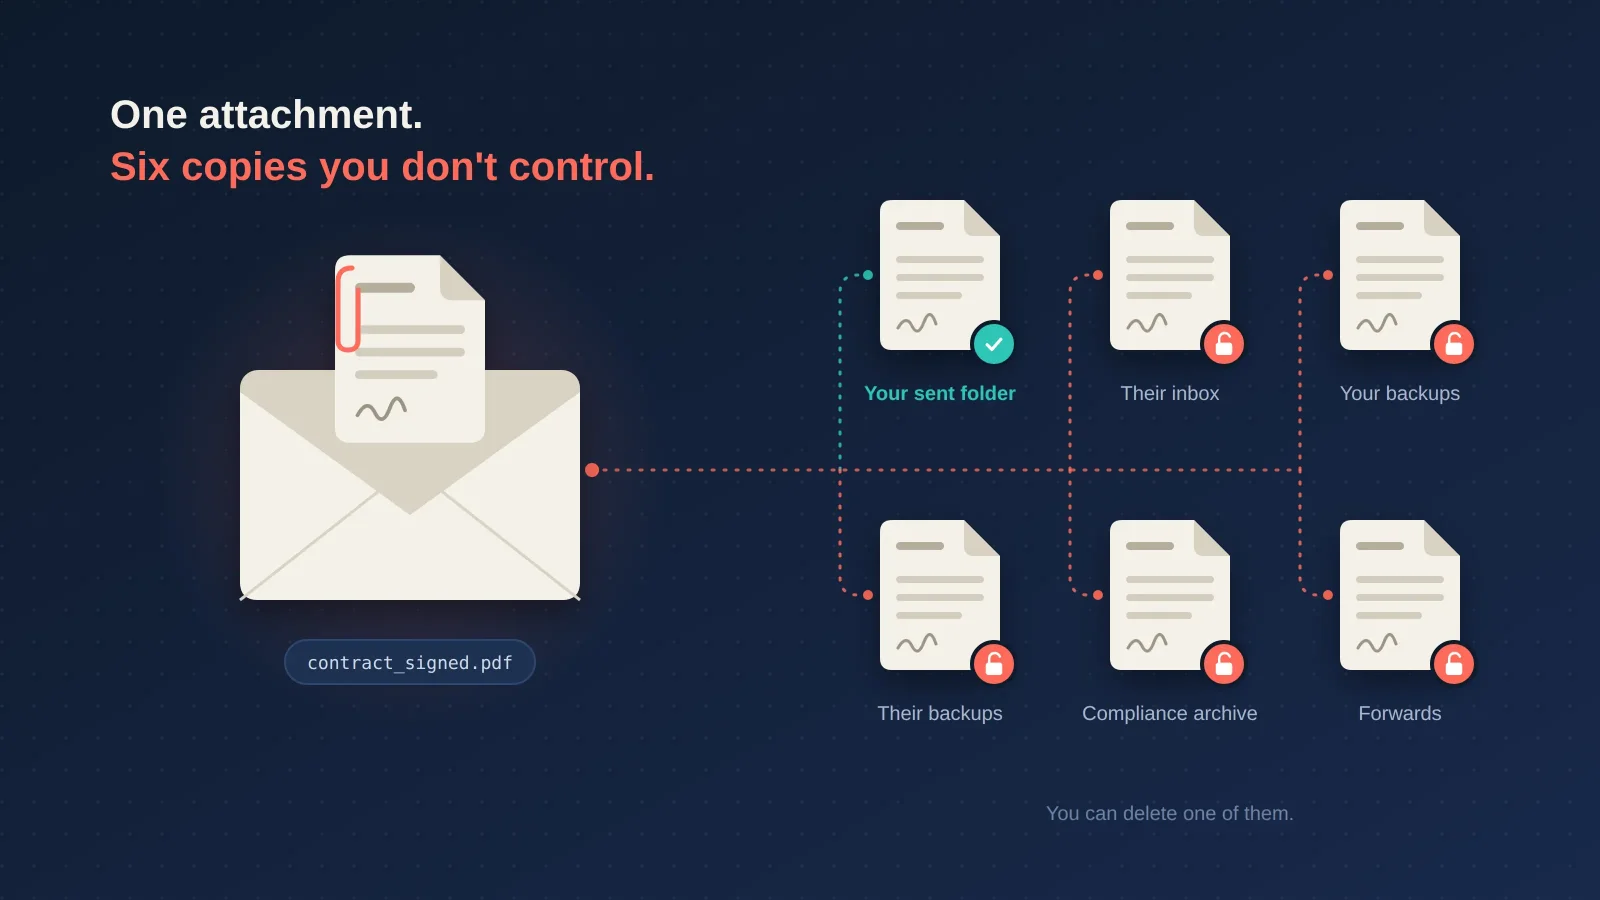
When you attach a contract to an email, you don't send a file. You create copies of it:
- one in your sent folder
- one in each recipient's inbox
- one in your organization's backups, and one in theirs
- one in each archiving or compliance system that captures mail
- one for every forward, including the one that goes to someone's personal account
Each copy has its own lifetime, its own access controls and its own breach risk, and you control exactly one of them. Deleting the email from your sent folder does nothing to the rest.
The practical risk isn't some exotic attack on email protocols. It's ordinary account compromise. When an attacker gets into a mailbox through phishing or a reused password, one of the first things they do is search it: "password", "contract", "invoice", "IBAN". Years of history make that search very productive.
Problem two: encryption is patchy and mostly invisible
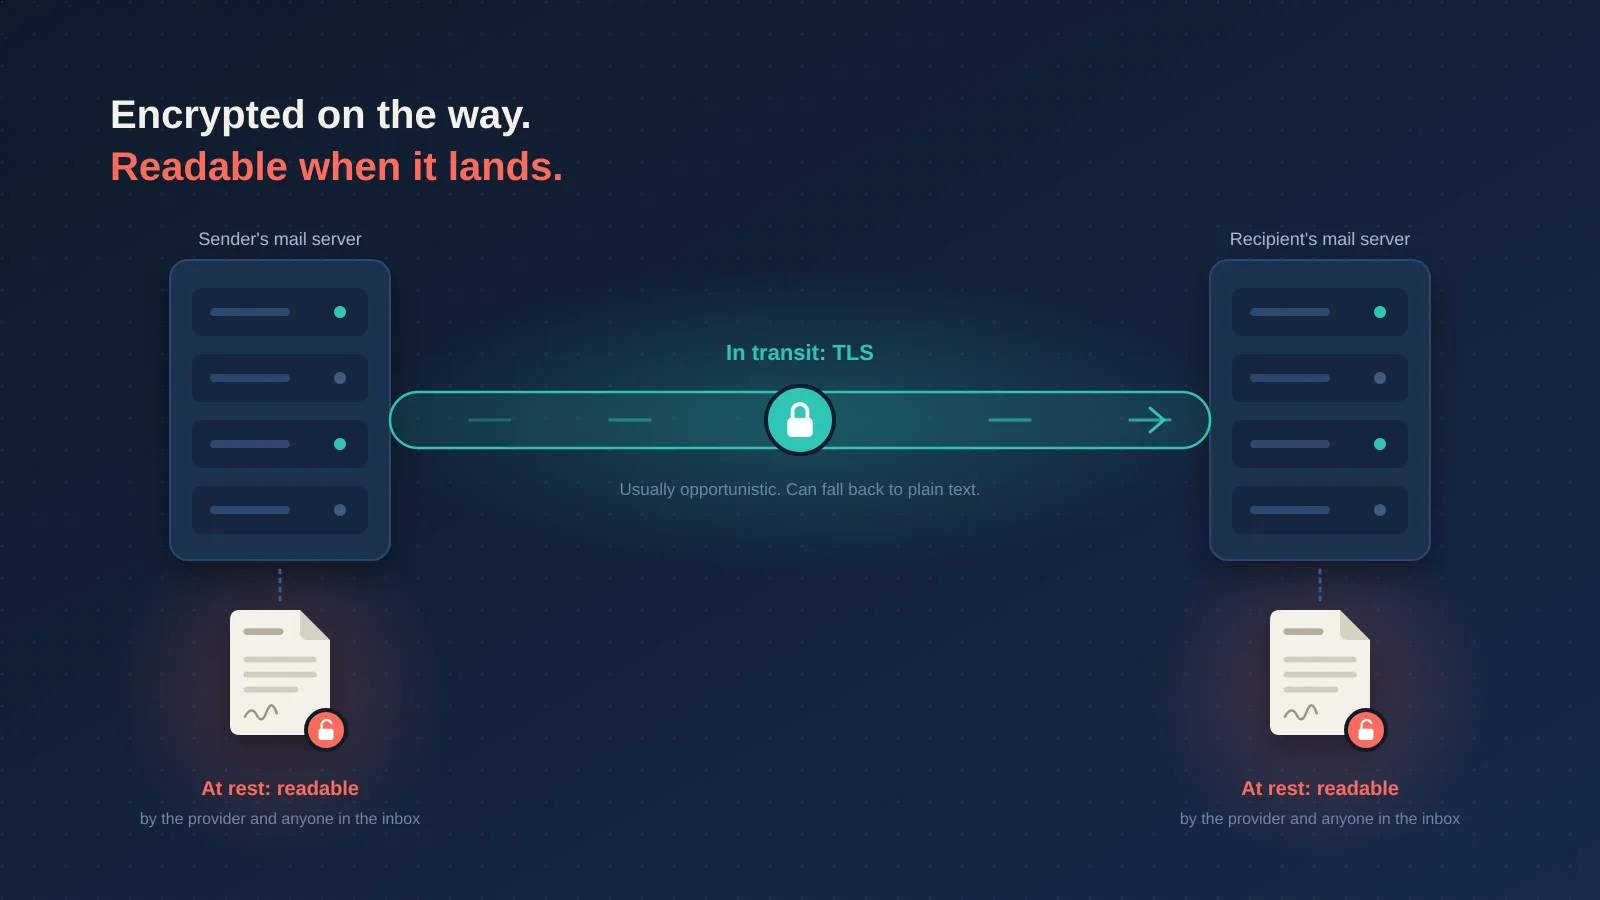
Most email today is encrypted between mail servers using TLS. That's a real improvement, but it has limits worth knowing:
- It's usually opportunistic. Servers use STARTTLS when both sides support it. Unless a domain enforces it (with something like MTA-STS), a misconfigured or tampered connection can fall back to plain text without anyone noticing.
- It protects the journey, not the destination. Once delivered, the message sits on mail servers in a form the provider can read. Encryption at rest, where it exists, uses keys the provider holds.
- End-to-end email encryption exists but rarely gets used. OpenPGP and S/MIME work, but both sides have to set up and manage keys. Outside of a few specialist circles, almost nobody does it with external partners.
So when people talk about "secret emails" or "encrypted email", they usually mean TLS in transit. That's good for the network part and does nothing about the six permanent copies.
Problem three: once you hit send, it's out of your hands
You can't unsend an email to an external address. You can't see whether the attachment was opened or forwarded, and you can't make it expire. Some providers offer "confidential mode" or expiring messages, but these typically only work inside the same provider, and recipients on other systems get a link to a portal instead, which is a different tool wearing an email costume.
That lack of control is fine for most of what we send. It's not fine for things that should exist only as long as they're needed.
Problem four: the password-protected ZIP
The classic workaround is to zip the file with a password and send the password separately. It's better than nothing, but in practice:
- the password often ends up in the same thread, or in a second email to the same inbox
- older ZIP encryption (ZipCrypto) is weak, and plenty of tools still default to it
- the encrypted ZIP still lives forever in every mailbox it reached, waiting for the password to leak later
- recipients on phones often can't open it at all
It solves the "sent in plain text" problem and leaves the "stored forever" problem exactly where it was. Many mail filters also quarantine encrypted ZIPs, because they can't scan inside them. There's more on that and other email attachment security risks in a separate post.
Secure document sharing: send a link, not the document
The better pattern is to keep the document out of email entirely and send a link that does three things:
- Encrypts the document on your device, so the service in between can't read it.
- Works once. The first person to open it gets the document; anyone else gets nothing.
- Deletes the document from the service after delivery, or at a deadline if it's never opened.
This is how Konfidant works. You drop the document in your browser, it's encrypted with AES-256-GCM before upload, and the decryption key is placed in the part of the link after the #, which browsers never send to a server. The recipient clicks the link, clicks "Open & decrypt", and the document is decrypted in their browser. The encrypted copy on Konfidant is then deleted.
What ends up in the email thread is a link. A year later, if someone breaks into that mailbox and searches for "contract", they find a link that returns an error.
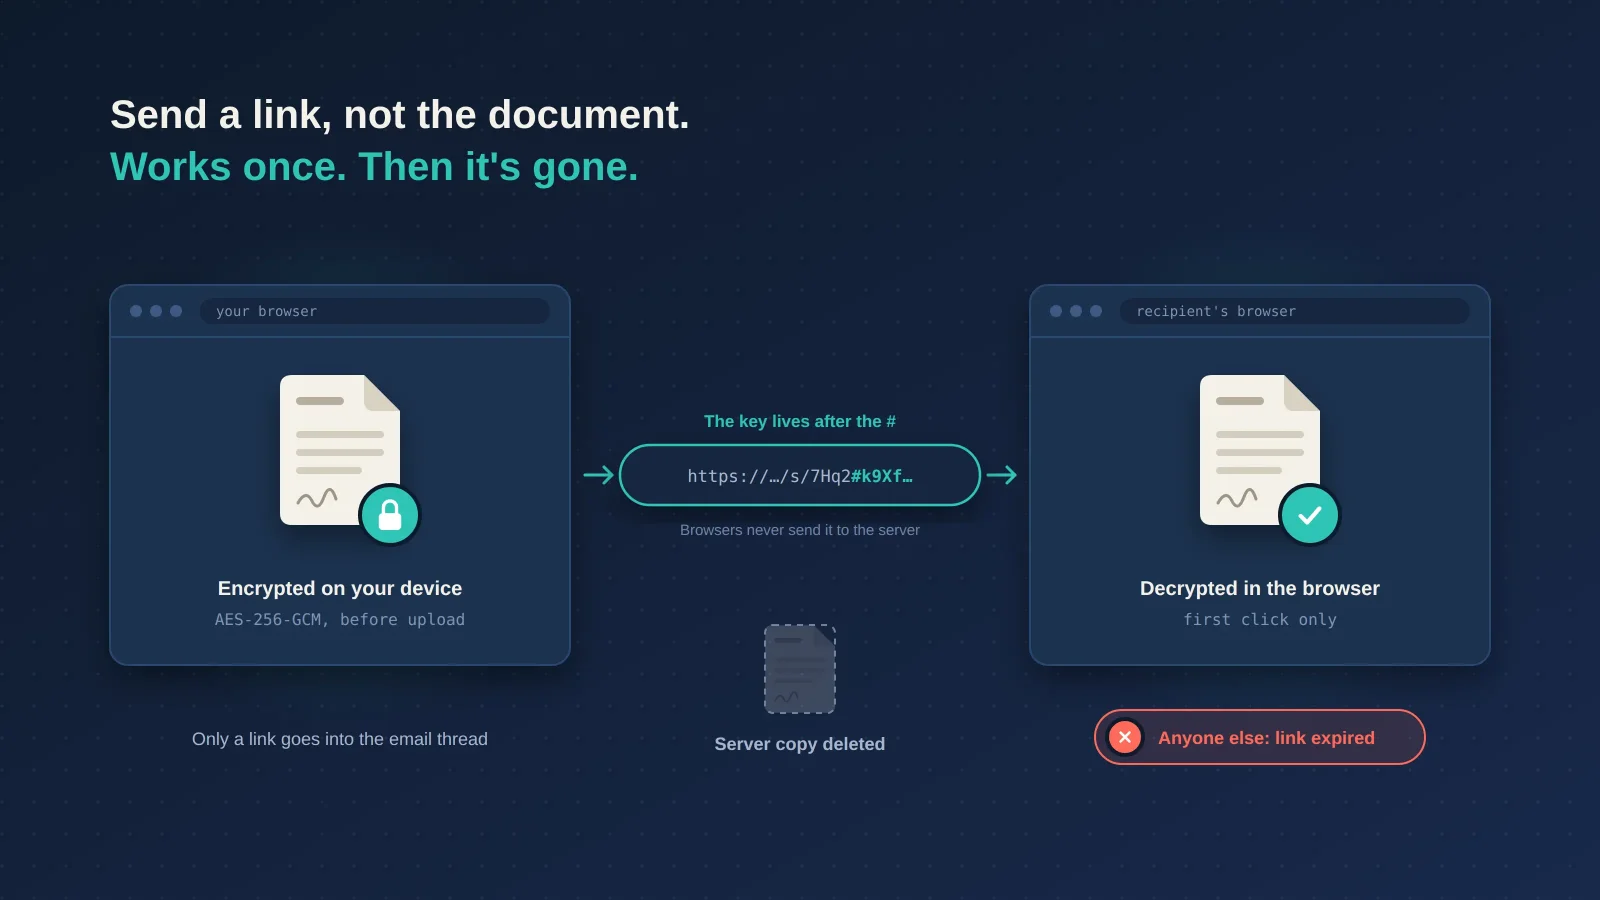
You can still use email to send the link. That's fine, and often the most natural way to reach an external client. The difference is that the email now carries a pointer that expires, not the document itself.
Email vs. a secure document sharing link
| Email attachment | One-time encrypted link | |
|---|---|---|
| Copies created | One per mailbox, backup and forward | One, temporarily, on the service |
| Readable by the providers in between | Yes | No, encrypted before upload |
| Works after the recipient opens it | Forever | No, it's single-use |
| Expires if never opened | No | Yes |
| Recipient needs special software | No | No, just a browser |
| Stops the recipient keeping a copy | No | No (nothing can) |
That last row matters. Neither email nor a one-time link can stop someone who received a document from saving or forwarding it. What a link removes is all the copies nobody intended: in backups, archives, forwarded threads and compromised inboxes.
When email is still fine
There's no need to be dogmatic. Email is the right tool for:
- everyday communication and documents that aren't sensitive
- anything both sides need to refer back to, like meeting notes and project updates
- formal records that must be kept, where your mail archive is part of how you meet that obligation
The rule of thumb is simple: if the document contains personal data, credentials, financial details or anything under NDA, send a link instead of an attachment.
Making the switch without annoying anyone
A few habits make this painless:
- Pick the documents that matter. Contracts, offer letters, payslips, ID scans, bank details, credentials. Leave everything else alone.
- Tell recipients what to expect. A one-line note ("You'll get a secure link from us; it works once and expires on Friday") stops people treating it as phishing.
- Use your own domain. On Konfidant's paid plans, links can come from
share.yourcompany.com, which recipients recognize and trust more than an unfamiliar service. - Clean up the past. Search your sent mail for "password", "IBAN" and "attached contract". Rotate any credentials you find.
There are pages for how legal teams, HR and finance typically make this change.
Questions people ask
Isn't TLS enough?
TLS protects the message on its way between servers. It doesn't change the fact that the document is then stored in several mailboxes and backups indefinitely, readable by anyone who gets into any of them.
What about encrypted email services?
Services built around end-to-end encrypted email are a good fit when both sides use them. For documents going to clients, auditors or candidates who use ordinary email, a link they can open in any browser is usually more practical.
Will recipients think the link is phishing?
Some might, especially the first time. A heads-up in your own words, a recognizable custom domain and a consistent habit all help. Konfidant also shows a clear page before anything is downloaded, rather than starting a download on load.
Can I send the link by email?
Yes. The link is single-use and expires, so once it's been opened, the email is harmless. Send it to the person directly rather than to a shared address.
To try it, send your first document free. For a broader look at sharing habits that cause trouble, see 5 mistakes that make it hard to send files securely.
This article provides general information, not legal advice. It describes Konfidant's features without guaranteeing them; what we provide is set out in our Terms of Service and Data Processing Agreement. Assess whether a tool meets your legal and regulatory requirements before sharing regulated data.
Enjoyed this article?
Get new articles on secrets management and secure sharing in your inbox. No spam, unsubscribe anytime.
We'll email you a link to confirm. Protected by Cloudflare Turnstile. See our Privacy Policy.
Ready to secure your team's secrets?
Stop leaving credentials in Slack. Start using burn-after-reading encryption.
Get started free