How to Share a Password Securely (Without Leaving It Lying Around)
Nobody wakes up wanting to share a password. It happens at 6:40 pm on a Thursday, when a colleague is locked out of the analytics dashboard and the person who set it up is on a plane. You have the password. They need it. Slack is open.
So you paste it, add "delete this after" in brackets, and get a thumbs-up back. Problem solved, as far as anyone can tell.
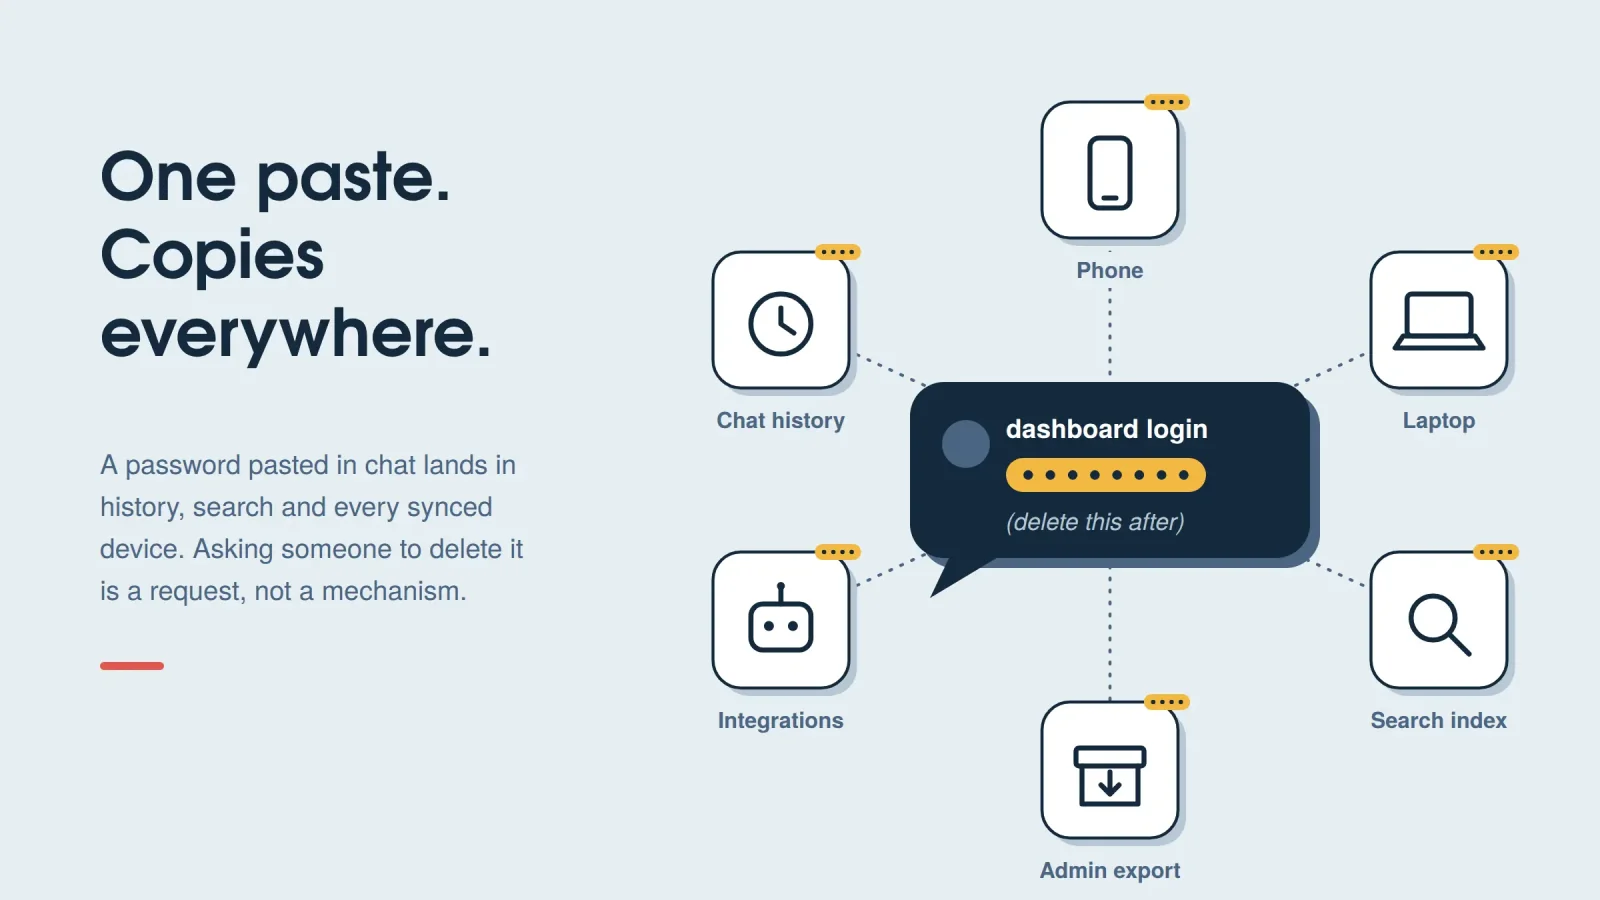
The trouble is what happens after the thumbs-up. That message now lives in your workspace's history, in Slack's search index, on every phone and laptop where either of you is logged in, and in any export an admin runs later. If the workspace has no retention policy (most paid workspaces keep everything by default), it stays there for as long as the workspace exists. "Delete this after" is a request, not a mechanism.
This post is about the mechanism. There are only a handful of good ways to share a password, and each one fits a different situation.
The four questions that decide how to share it
Before picking a tool, it helps to be honest about what you are actually doing:
- Does the person need it once, or forever? A one-off login to fix something is different from joining a team that uses the account daily.
- Could they have their own account instead? If yes, that beats any sharing method.
- How bad is it if this leaks? A Wi-Fi password and a production database root password are not the same conversation.
- Can you rotate it afterwards? If changing the password is a two-minute job, you have a lot more room for error.
Most bad password sharing comes from treating every case like the easiest one.
Option 1: a one-time secret link
A one-time secret is a link that reveals its contents exactly once. You paste the password into a tool, it gives you a URL, you send the URL. When the recipient opens it, the secret is shown and the link dies. Anyone who opens it later, including someone scrolling back through the chat next year, gets nothing.
The idea isn't new. Open-source tools like Onetime Secret and PrivateBin have offered it for years, and plenty of security teams self-host one. What matters is how a given tool handles the secret in the meantime, because "one-time" says nothing about who can read it before it's opened.
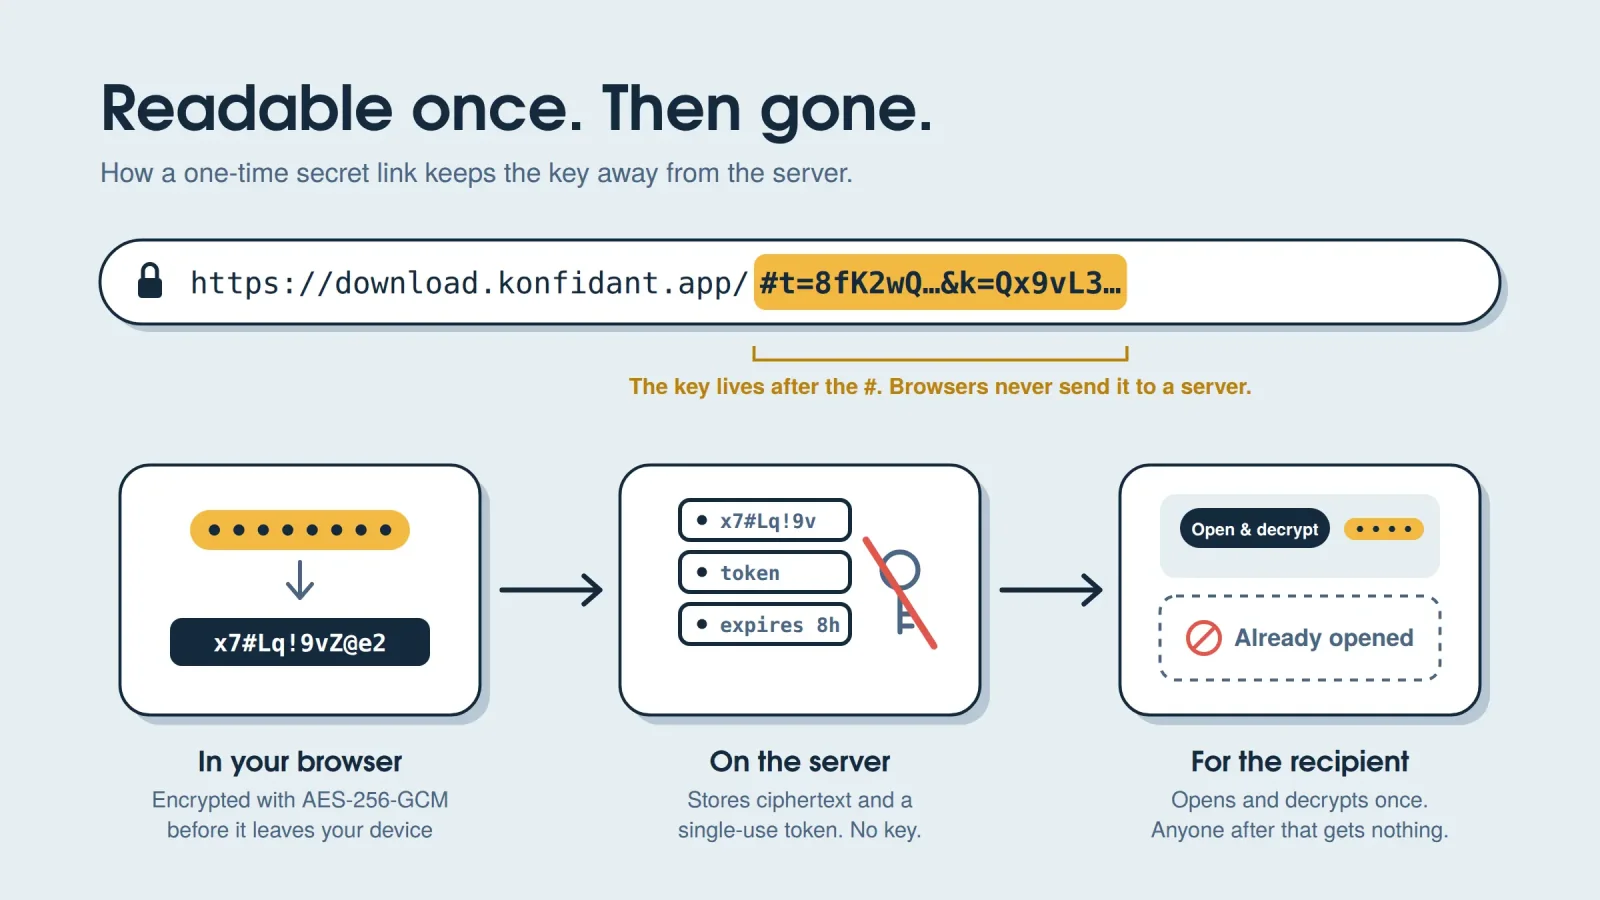
That's the part worth checking. With Konfidant, the password is encrypted in your browser with AES-256-GCM before it's uploaded. The decryption key goes into the part of the link after the #, which browsers never send to a server. So the link looks like this:
https://download.konfidant.app/#t=<token>&k=<key>
The server stores ciphertext and a single-use token. It never sees the key, so it can't read the password even if it wanted to. When the recipient clicks "Open & decrypt", the token is consumed, their browser decrypts the password locally, and the stored ciphertext is deleted. If nobody opens it, it expires on its own (8 hours on the free plan, up to 7 or 30 days on paid plans).
One-time secret links are the right choice when:
- someone needs a password once, today
- the recipient is outside your company and has no access to your password manager
- you're handing over a credential they'll immediately change, like an initial login
A few things they don't do. They don't stop the recipient from copying the password somewhere else after opening it. They don't protect a link that ends up in the wrong hands before it's opened, because whoever opens it first gets the secret. That's why you send the link directly to the person (a DM, an email to them, a ticket assigned to them) and not to a busy channel.
There's a useful side effect, though. If the recipient clicks the link and sees "already opened", you know someone else got there first. Rotate the password and send a new link. A password pasted in plain text gives you no such signal.
Option 2: a password manager's sharing feature
If someone needs a password on an ongoing basis, a one-time link is the wrong tool. They'll ask you again next week, and the week after.
This is what password managers are good at. 1Password, Bitwarden and most of their peers let you put shared credentials in a vault or collection, grant access by group, and remove access when someone leaves. You get one place to rotate a password and everyone with access gets the new one.
The usual failure mode is over-sharing. It's easy to give a contractor access to "Engineering" when they needed one login in it. Make small vaults, organized by who needs them rather than by which tool the password belongs to, and review them when people change roles.
Password managers also have their own one-off sharing features (Bitwarden Send, 1Password's shareable item links, for example). They work fine if both sides already use that manager. One-time secret tools fill the gap when the other side doesn't, which with clients, vendors and freelancers is most of the time.
Option 3: don't share the password at all
The best password to share is one that doesn't need sharing. Before sending anything, check whether you can:
- Create an individual account. Most SaaS tools support multiple users, even if it costs a seat. Individual accounts give you an audit trail and a clean off-boarding step.
- Use SSO. If your company has an identity provider, adding the tool to it means access follows the person, not the password.
- Issue temporary credentials. Cloud platforms do this natively. On AWS, STS issues temporary credentials that expire on their own. Many databases let you create a time-limited role. A credential that expires in four hours is much less interesting to an attacker than one that never does.
Shared logins are sometimes unavoidable: a legacy admin panel, a vendor portal that charges per seat, a router. For those, combine options 1 and 2: keep the password in a vault, and use a one-time link when you have to hand it to someone outside it.
Option 4: a phone call (for the truly sensitive ones)
For the handful of credentials where a leak would be a disaster (root keys, recovery codes, the master password to a vault), reading it out over a verified phone call or in person is still a reasonable choice. Nothing is written down anywhere, which is the point.
It's slow and error-prone with long random strings, so it doesn't scale. A middle ground some teams use: send the one-time link, then confirm by phone that the right person opened it.
What not to do, briefly
You already know most of these, but each has a specific problem worth naming:
- Plain-text chat (Slack, Teams). Searchable, synced to every device, retained by default, included in admin exports on some plans, and readable by any integration with message access.
- Email. Stored in two mailboxes plus their backups, easily forwarded, and inboxes are what phishing attacks aim for. If an attacker gets into a mailbox, searching for "password" is one of the first things they do.
- SMS. Messages sit on both phones, show up on lock screens, and phone numbers can be hijacked through SIM swapping.
- Shared docs. A "Logins" page in Notion or a Google Doc is a password manager without any of the security. Everyone with access to the doc has every password in it, plus the full version history.
- Splitting the password across two channels. Half in Slack and half in email feels clever, but now it's stored permanently in two places instead of one.
A simple rule for teams
Policies that run to four pages get ignored. Something like this fits in one Slack message and covers most cases:
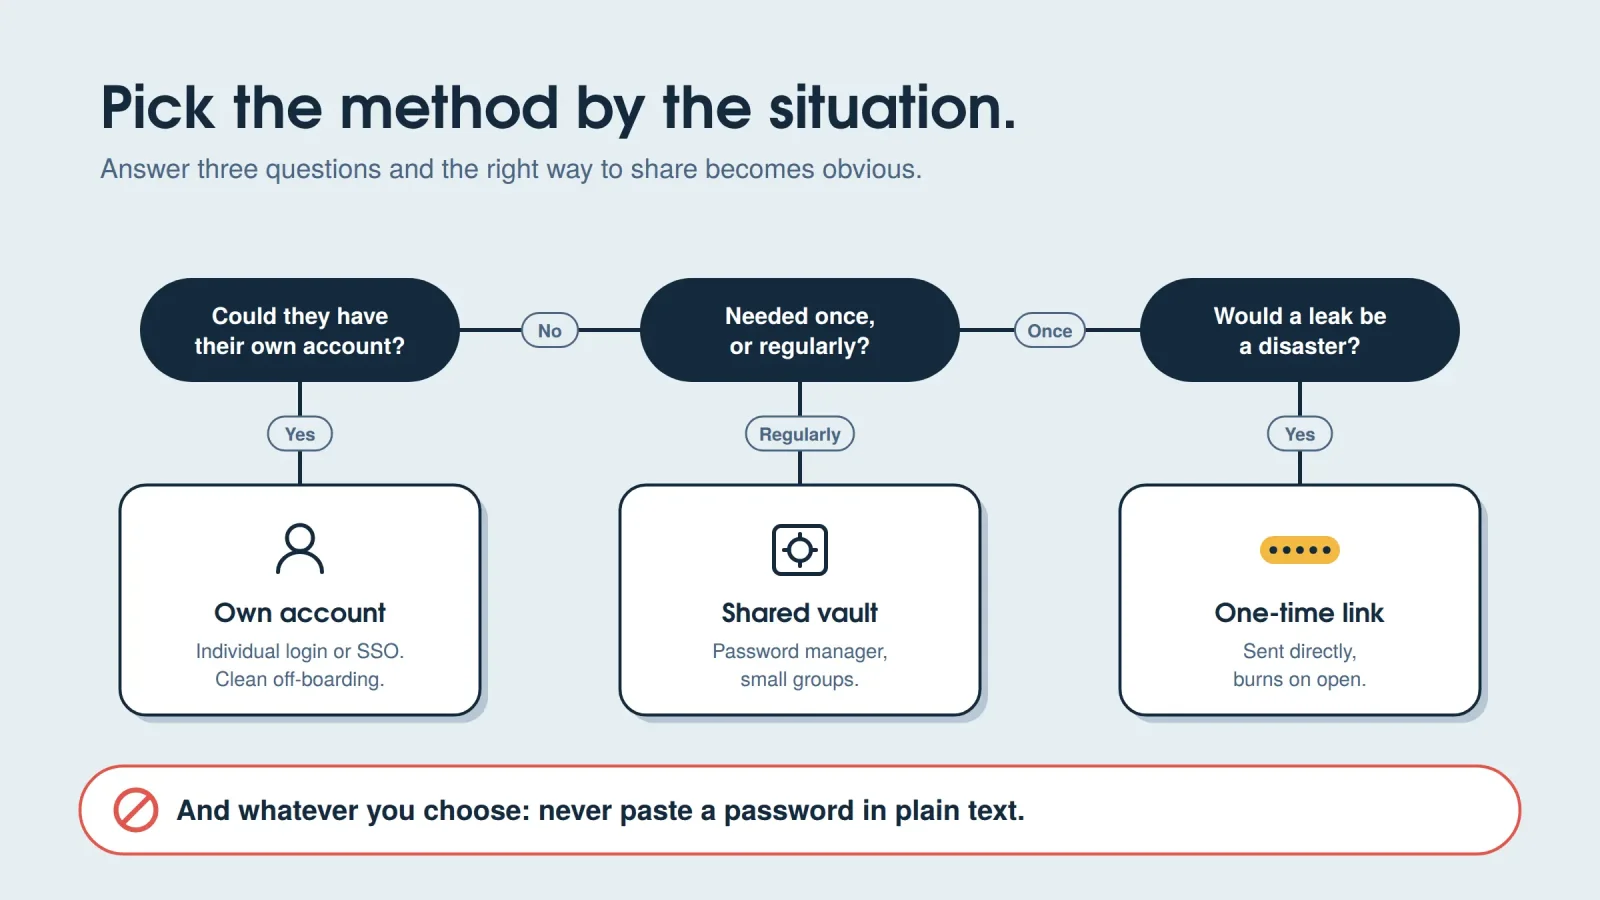
If someone needs it once, send a one-time link. If they need it regularly, put it in the vault. If they could have their own account, give them one. Never paste a password in plain text.
Then make the right tool the easiest one. If your team has to log in to three systems to send a secret, they'll go back to pasting it in Slack by Friday.
Cleaning up what's already out there
If you've been on a team for more than a few months, there are passwords in your chat history right now. A ten-minute cleanup goes a long way:
- Search your Slack or Teams history for "password", "pw", "login" and "pass:". Do the same in your sent email.
- For anything you find that's still valid, rotate it. Deleting the message is nice, but rotation is what actually closes the hole.
- Move anything that's shared regularly into a password manager.
- Agree on the one-line rule above and pin it somewhere.
Questions people ask
Is a one-time secret link safe to send over Slack?
Safer than the password itself, as long as you send it in a direct message to the right person. The link stays in Slack's history, but once it's been opened or has expired, it's useless. The risk window is the time between sending and opening, which is usually minutes.
What if the recipient opens the link and loses the password?
Then you send a new one. There's no way to re-open a burned link, by design. If this happens often, the credential probably belongs in a shared vault rather than in one-time links.
Can I see if my link was opened?
The recipient seeing "already opened" tells them. On Konfidant's Enterprise plan, verified burn also records the time each share was opened, without recording who opened it or from where.
Do I need an account to receive a one-time secret?
Not with Konfidant. Recipients just open the link in a browser. The sender needs an account, and the free plan is enough to start.
Should I still rotate the password after sharing it?
If it was a temporary handover, yes. If someone is joining a shared account permanently, rotate when someone leaves instead. And rotate immediately if a link shows as already opened when your recipient tries it.
If you want to try the one-time approach, Konfidant's free plan gets you a working link in under a minute. For the developer-specific version of this problem (API keys, .env files, SSH keys), see how to share API keys without leaving them in Slack.
This article provides general information, not legal advice. It describes Konfidant's features without guaranteeing them; what we provide is set out in our Terms of Service and Data Processing Agreement. Assess whether a tool meets your legal and regulatory requirements before sharing regulated data.
Enjoyed this article?
Get new articles on secrets management and secure sharing in your inbox. No spam, unsubscribe anytime.
We'll email you a link to confirm. Protected by Cloudflare Turnstile. See our Privacy Policy.
Ready to secure your team's secrets?
Stop leaving credentials in Slack. Start using burn-after-reading encryption.
Get started free