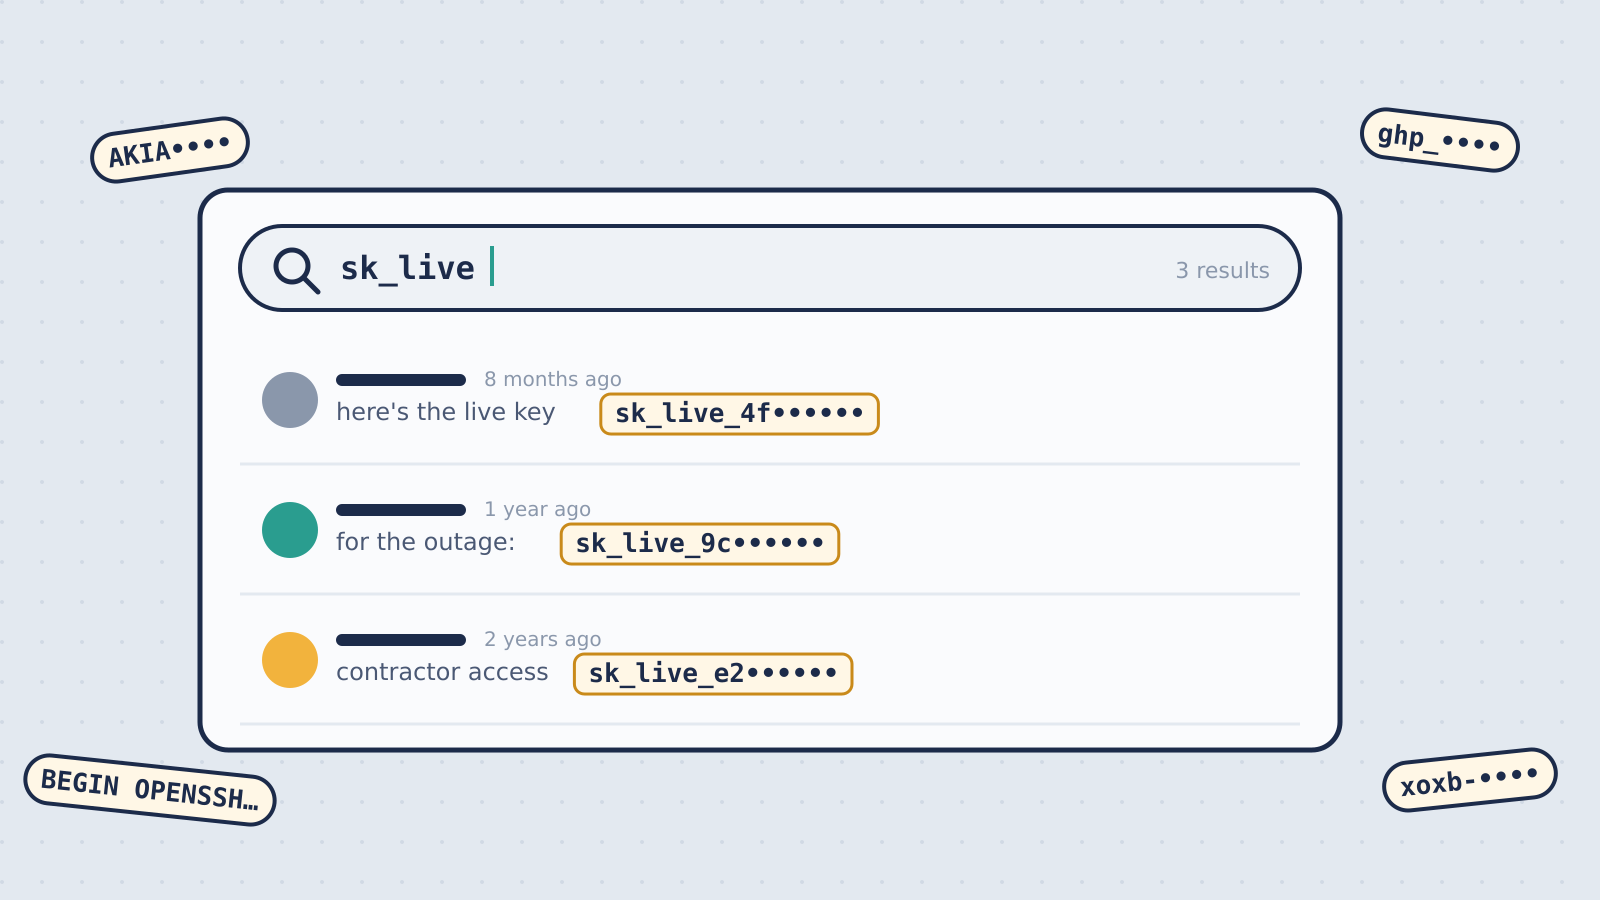
Open your team's Slack and search for sk_live. Then try AKIA, ghp_, xoxb- and BEGIN OPENSSH PRIVATE KEY.
If you got zero results, congratulations, you're in a rare team. Most people find something, and it's usually not old. A Stripe key a backend dev needed during an outage. An AWS access key for a contractor who was "only around for two weeks" last spring. A .env file someone dropped in a thread so the new hire could get the app running on day one.
None of these were bad decisions in the moment. The key was needed, Slack was open, and the alternative was a ten-minute detour. The problem is that the secret outlives the moment by months or years, and nobody rotates a key they forgot they shared.
Where a pasted key actually ends up
When you paste an API key into a Slack DM, it goes into:
- the workspace's message history, kept indefinitely unless an admin set a retention policy
- Slack's search index, so anyone with access to the conversation can find it by typing
key - the local cache of every device where you or the recipient are logged in
- any workspace export, and any bot or integration with permission to read that conversation
Deleting the message later helps a little. It doesn't help with whoever already saw it, synced it or exported it. Email is worse: two mailboxes, two sets of backups, and a forward button.
The .env case deserves its own warning. A whole file of secrets is easy to commit by accident. GitHub's secret scanning catches many well-known key formats and can block the push, but scanning catches patterns, not everything, and a key that made it into history needs rotating no matter what you do to the commit.
Match the tool to the situation
There's no single right way to share secrets. There are three common situations, and each has a tool that fits.
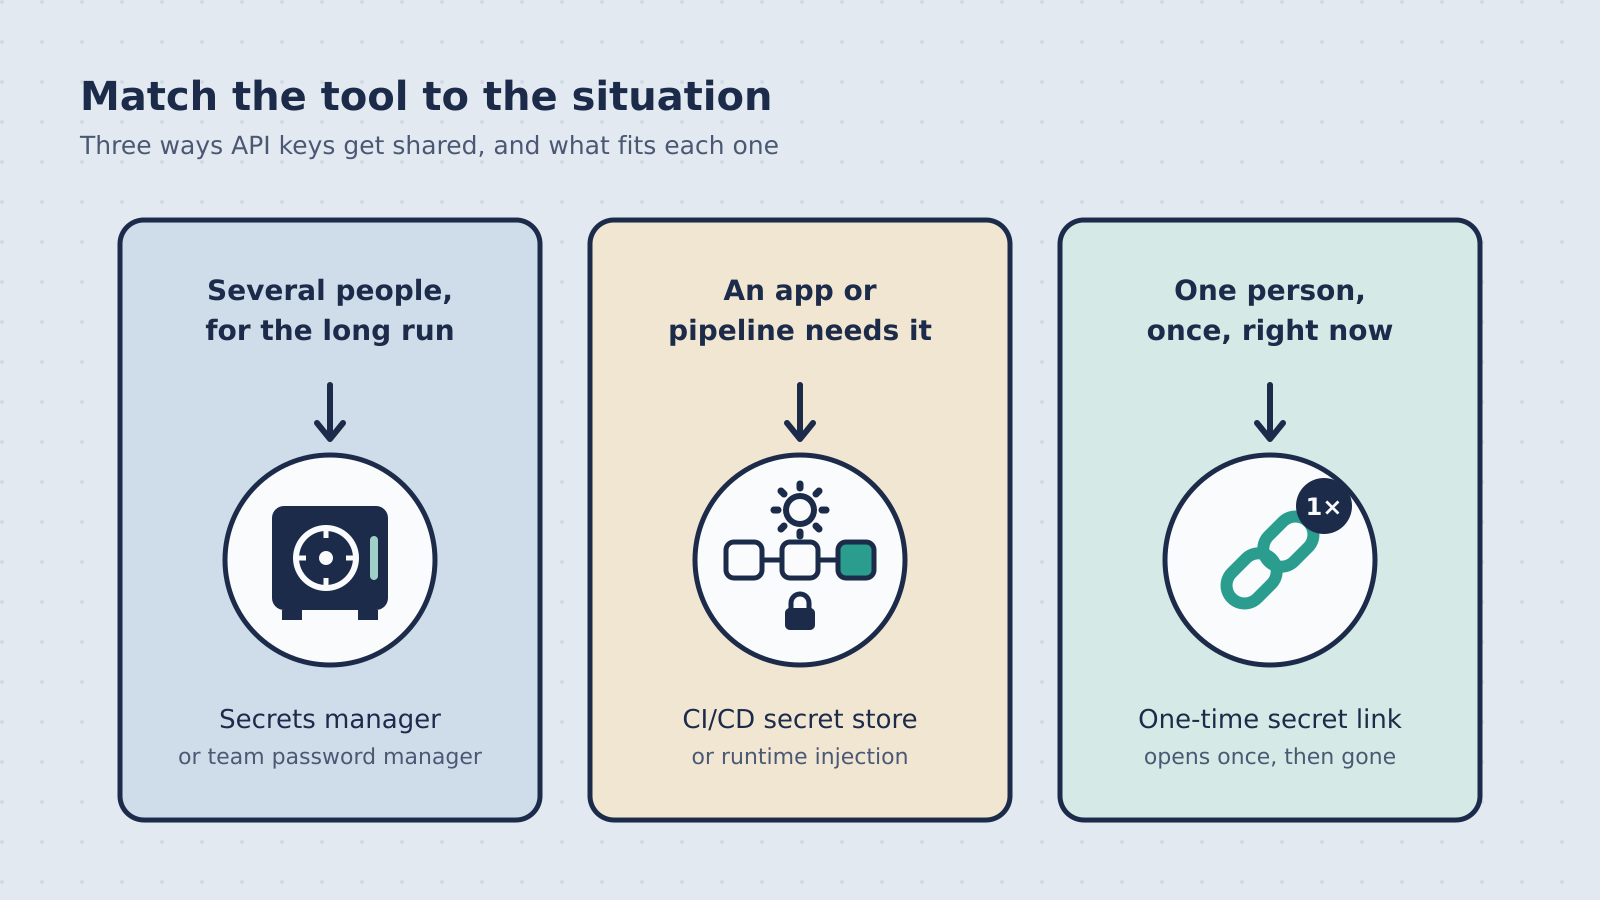
"Several people need this key, for the foreseeable future"
That's a job for a secrets manager or a team password manager: HashiCorp Vault, AWS Secrets Manager, 1Password, Bitwarden, or whatever your platform already provides. Access is granted by group, rotation happens in one place, and when someone leaves you remove them from the group instead of hunting through chat.
The trap here is over-broad access. If everyone in engineering can read the production payment key, you haven't really shared one secret, you've shared it with forty people. Split by environment and role.
"My app or pipeline needs this key"
Then a human shouldn't be passing it around at all. Put it in your CI/CD secret store (GitHub Actions secrets, GitLab CI/CD variables and so on) or inject it at runtime from your secrets manager. Add .env to .gitignore, and run a scanner like gitleaks or trufflehog in CI so a slip gets caught before it lands on main.
"One person needs this once, right now"
This is the case that ends up in Slack, because the first two options feel like too much ceremony. A new hire needs the staging credentials before their vault access is approved. A contractor needs one key for one integration. You're on call and a teammate needs the database password to run a migration.
For these, a one-time secret link is the tool. You paste the key, get a link, send the link. The recipient opens it once and the content is gone. If the link resurfaces in a search six months later, it opens to nothing.
With Konfidant, the encryption happens before anything leaves your machine. Your browser encrypts the secret with AES-256-GCM and puts the key in the link fragment (the part after #), which browsers never send to a server. Konfidant stores ciphertext and a single-use token, and deletes the ciphertext right after the recipient opens it. The recipient doesn't need an account.
Two habits make this work well:
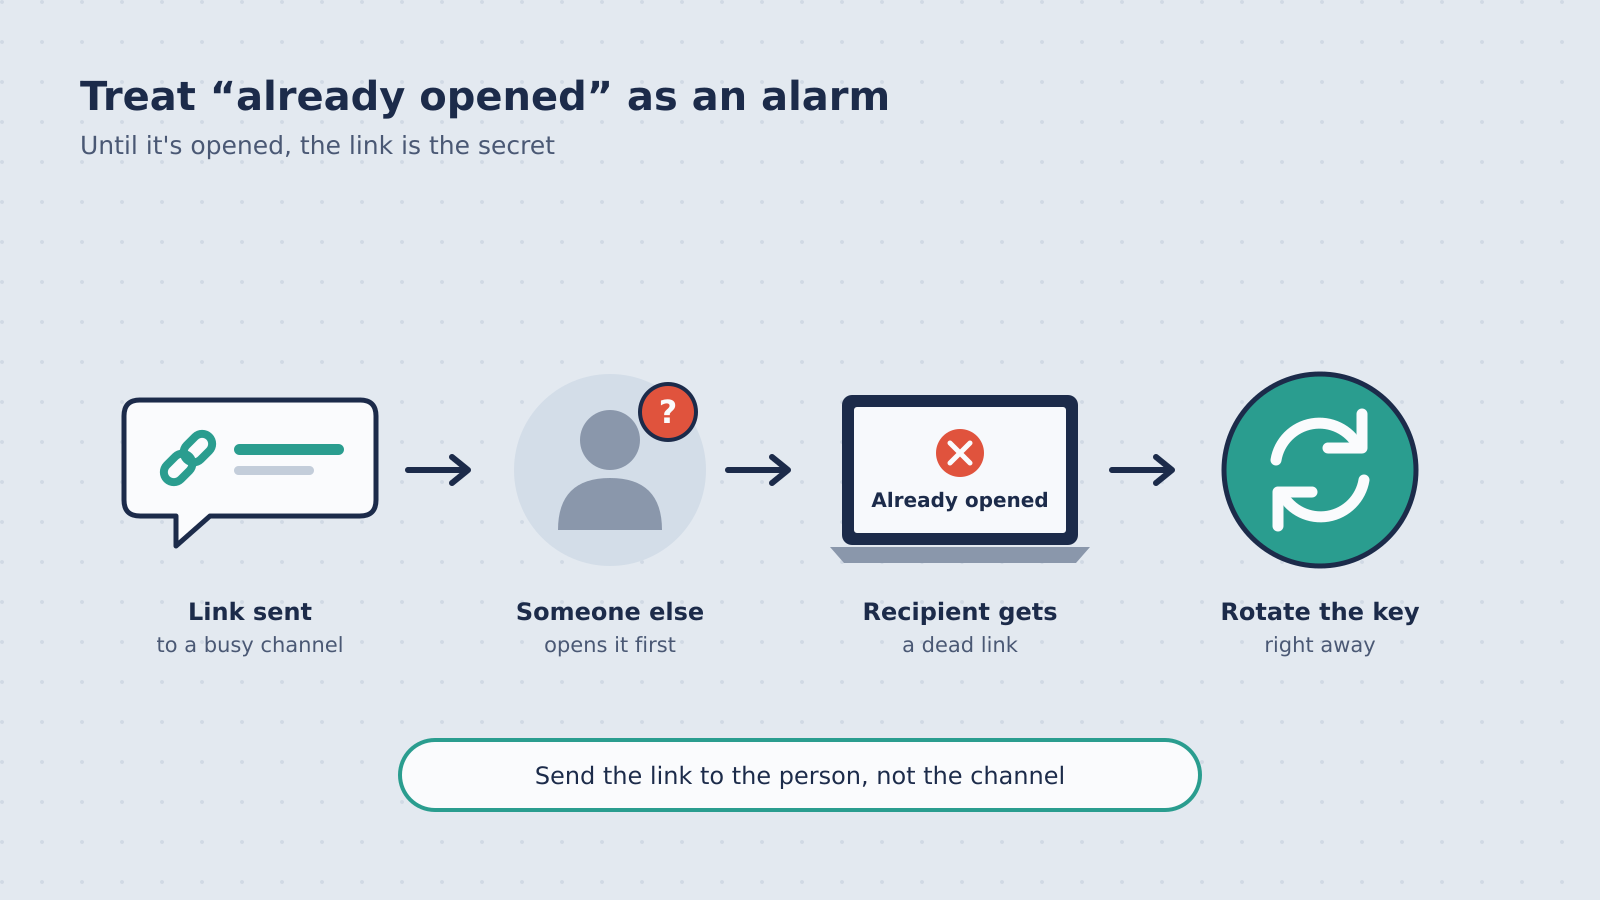
- Send the link to the person, not the channel. Until it's opened, the link is the secret. Whoever clicks it first gets the key.
- Treat "already opened" as an alarm. If your recipient gets a dead link they never opened, someone else did. Rotate the key.
Doing it from the terminal
Pasting into a browser is fine for occasional use. If you share secrets as part of a workflow (onboarding scripts, provisioning a client environment, rotating a key and handing the new one to a vendor), the browser becomes the slow part.
Konfidant has a REST API and official SDKs for JavaScript, Go, Python and Ruby on the Premium and Enterprise plans. The SDKs encrypt on your machine, so the plaintext and the key never reach Konfidant, and you don't depend on code served to a browser. A script can generate a fresh key, wrap it in a one-time link with a 4-hour expiry, and post the link to the new hire's DM. The API docs have the details.
A ten-minute cleanup for this week
If your search at the top of this post turned something up, here's a reasonable order of operations:
- Rotate first, delete second. Any live key you found in chat or email should be considered exposed. Deleting the message doesn't un-expose it.
- Check your repos. Run gitleaks or trufflehog against full history, not just the current tree.
- Move long-lived shared keys into a secrets manager and remove them from wherever they were living (wiki pages are a common hiding spot).
- Agree on a team rule. "Shared regularly: vault. Used by a pipeline: CI secrets. Needed once: one-time link. Never plain text in chat." Pin it in the engineering channel.
The rule only sticks if the right path is also the fastest one. That's the reason to have a one-time secret tool bookmarked at all: it's the thing people reach for at 7 pm when the vault request is still pending.
Questions people ask
Is it OK to share a test or staging key in Slack?
Staging keys often have more access than people think (real third-party sandboxes, copies of production data, the same cloud account). If it would take you more than a minute to say what the key can do, treat it like a production key.
What about sharing an SSH private key?
Ideally you don't. Each person should have their own key pair, and you add their public key to the server. If you really must hand over a private key (a shared deploy key for a legacy box, for example), send it as a one-time file share and replace it as soon as you can.
Can a one-time link be opened by Slack's link preview?
Not with Konfidant. Loading the page doesn't release the content. The recipient has to click "Open & decrypt", so link previews and email security scanners don't burn the share.
How long should the link stay valid?
As short as is practical. If your recipient is online, an hour is plenty. The free plan allows up to 8 hours, Premium up to 7 days and Enterprise up to 30 days. Unopened links expire and their ciphertext is deleted.
For the same problem with passwords rather than keys, see how to share a password securely. For how engineering teams use Konfidant day to day, there's a page for developers. Or send your first one-time secret free.
This article provides general information, not legal advice. It describes Konfidant's features without guaranteeing them; what we provide is set out in our Terms of Service and Data Processing Agreement. Assess whether a tool meets your legal and regulatory requirements before sharing regulated data.
Enjoyed this article?
Get new articles on secrets management and secure sharing in your inbox. No spam, unsubscribe anytime.
We'll email you a link to confirm. Protected by Cloudflare Turnstile. See our Privacy Policy.
Ready to secure your team's secrets?
Stop leaving credentials in Slack. Start using burn-after-reading encryption.
Get started free